
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
Get SaaSFrame Pro
Monthly
$18
Quarterly
$48
Yearly
$180
Upgrade to access this feature
Browse all screens & flows
Filter and search screens & flows
Access Figma files
Access mobile versions
Bookmark screens & flows
Join now
Search SaaS UI & UX Design Examples
Search thousands of real SaaS screens by keyword, category, industry, or product. Discover relevant UI patterns and find inspiration faster.
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
:











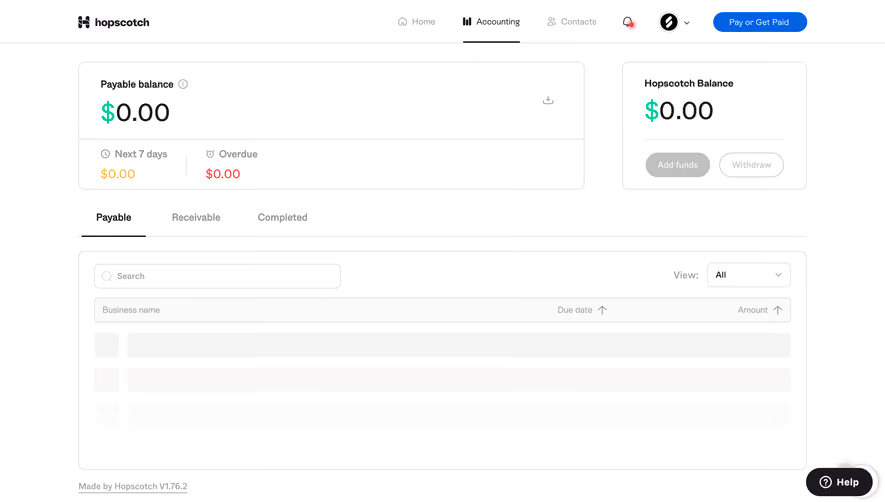

Dashboard
Hopscotch
Dashboard
Product
hopscotch O Payable balance $0.00 Home Accounting 0) O Overdue $0.00 Receivable Contacts Due date Q O Pay or Get Paid Hopscotch Balance O Next 7 days $0.00 Payable a Search Completed $0.00 Add funds View: Business name Made by Hopscotch V 1.76.2 Withdraw All Amount O Help
Advertising & Campaign Management
FinTech
Payments & Invoicing

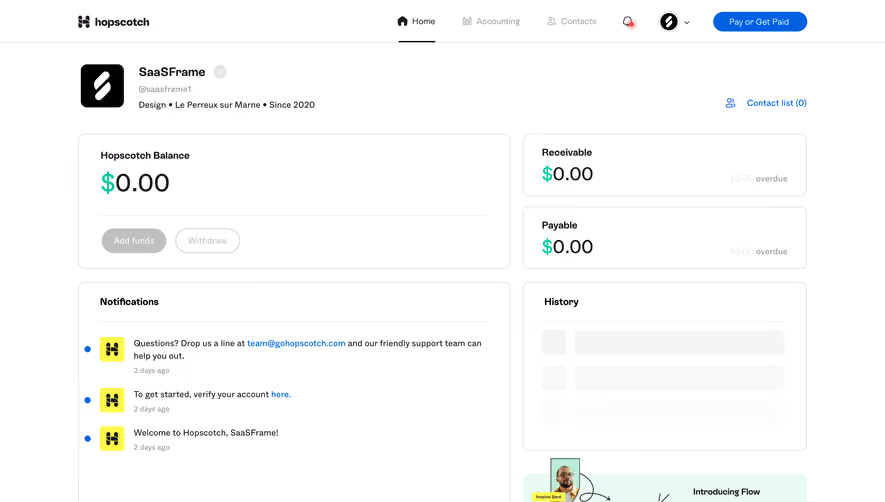


Account Setup
Hopscotch
Account Setup
Product
hopscotch Finish verification O Hidden and encrypted with bank-level security. We need you to upload supporting documents so that our team can verify your account. Antoine Milkoff's identification This can be your passport, drivers licence or state ID. Attachments O Add up to 5 files 5 files are the maximum number of files you can drop or select here zendesk -2,500.00 Quantum Marketing @quantum Send I'll do this later Made by Hopscotch V 1.76.2 +2,500.00 O Help
Advertising & Campaign Management
FinTech
Payments & Invoicing


Account Setup
Hopscotch
Account Setup
Product
hopscotch Link your bank account O Hidden and encrypted with bank-level security. g Add and connect instantly Done Need help? Contact support Connect your bank Hopscotch uses Plaid to securely connect to your bank account. You can add and remove accounts later in your Settings page. More @ Last thing!
Advertising & Campaign Management
FinTech
Payments & Invoicing

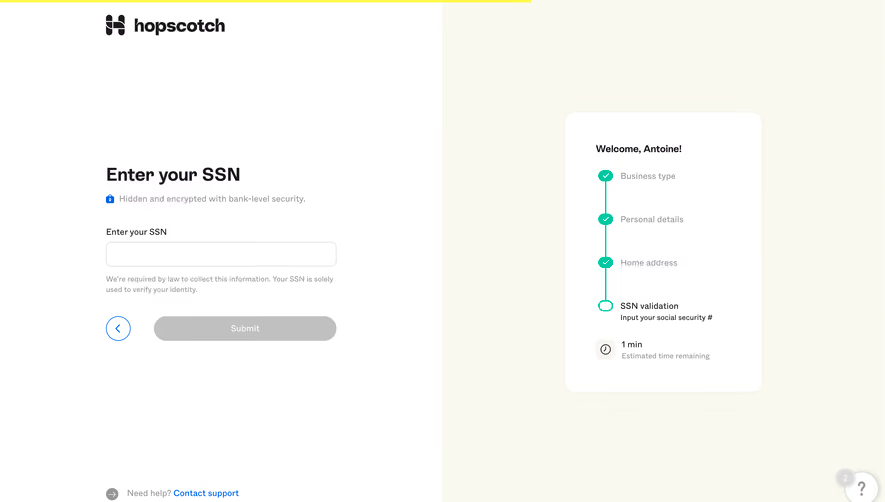
Account Setup
Hopscotch
Account Setup
Product
hopscotch Enter your SSN O Hidden and encrypted with bank-level security. Enter your SSN We're required by law to collect this information. Your SSN is solely used to verify your identity. Submit Need help? Contact support Welcome, Antoine! Business type Personal details Home address SSN validation Input your social security # 1 min Estimated time remaining
Advertising & Campaign Management
FinTech
Payments & Invoicing

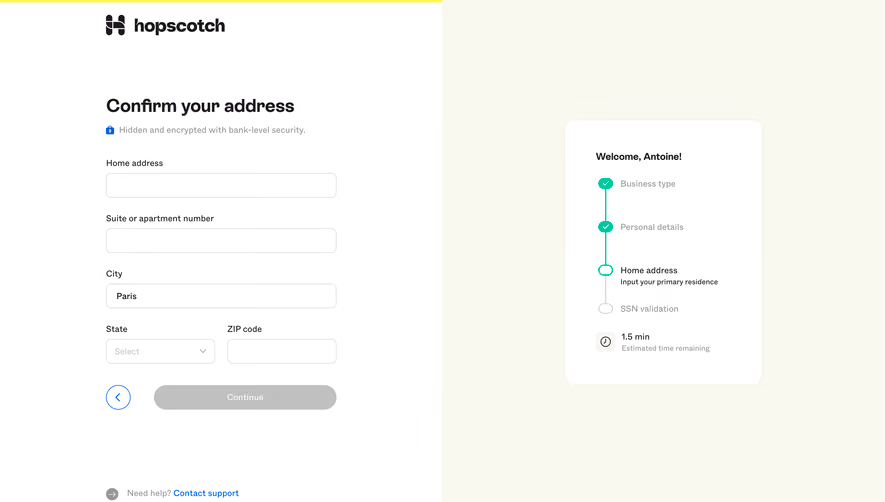
Account Setup
Hopscotch
Account Setup
Product
hopscotch Confirm your address O Hidden and encrypted with bank-level security. Home address Suite or apartment number City Paris State Select Welcome, Antoine! Business type Personal details Home address Input your primary residence SSN validation 1.5 min Estimated time remaining ZIP code Continue Need help? Contact support
Advertising & Campaign Management
FinTech
Payments & Invoicing

Account Setup
Hopscotch
Account Setup
Product
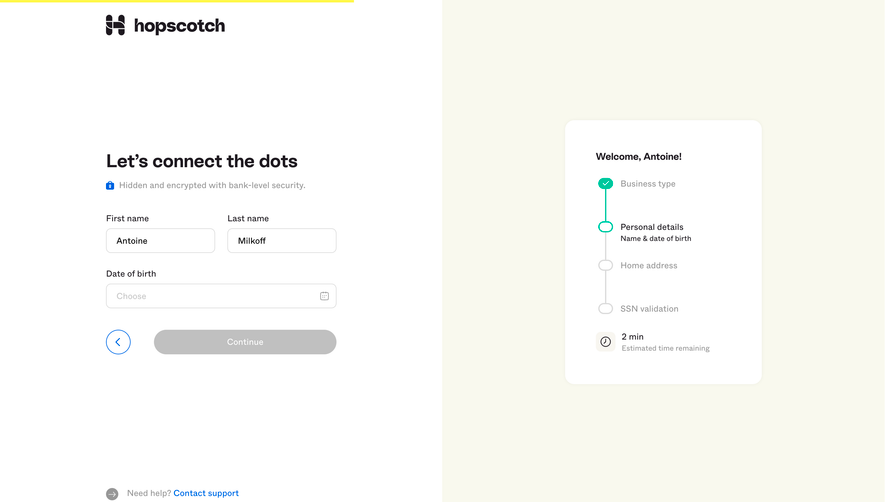
hopscotch Let's connect the dots O Hidden and encrypted with bank-level security. First name Antoine Date of birth Choose Last name Milkoff Continue Welcome, Antoine! Business type Personal details Name & date of birth Home address SSN validation 2 min Estimated time remaining Need help? Contact support
Advertising & Campaign Management
FinTech
Payments & Invoicing

Account Setup
Hopscotch
Account Setup
Product
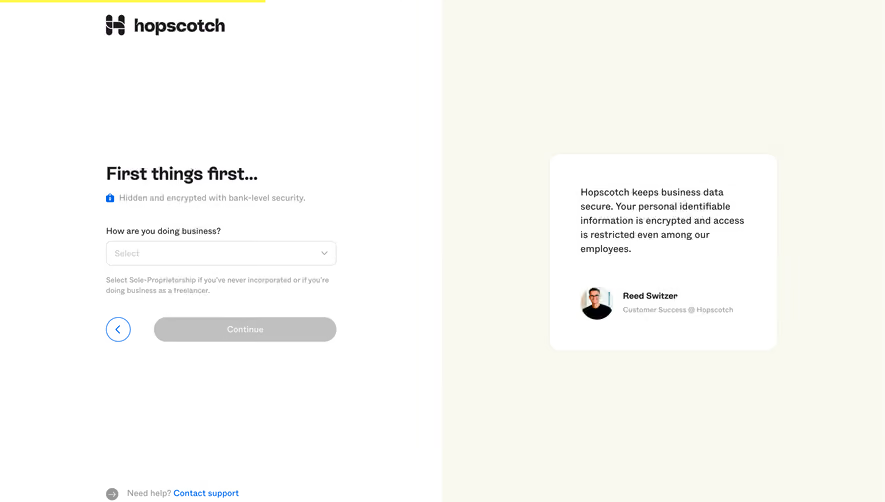
hopscotch First things first... O Hidden and encrypted with bank-level security. How are you doing business? Select Select Sole-Proprietorship if you've never incorporated or if you're doing business as a freelancer. Continue Need help? Contact support Hopscotch keeps business data secure. Your personal identifiable information is encrypted and access is restricted even among our employees. Reed Switzer Customer Success @ Hopscotch
Advertising & Campaign Management
FinTech
Payments & Invoicing



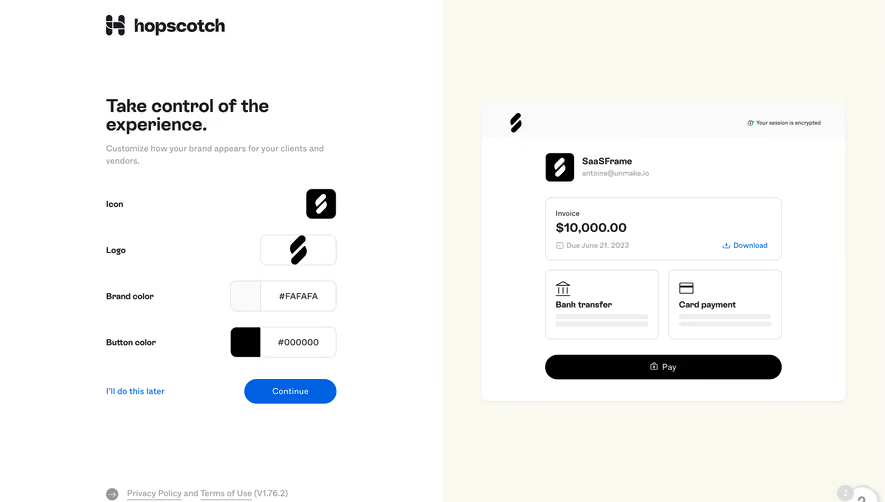
Appearance Customization
Hopscotch
Appearance Customization
Product
hopscotch Take control of the experience. Customize how your brand appears for your clients and vendors. loon Logo Brand color Button color I'll do this later SaaSFrame [email protected] Invoice $10,000.00 Due June 21, 2023 Ill Bank transfer tj Your session is encrypted Download Card payment #FAFAFA #000000 Continue Pay Privacy Policy and Terms of Use (Vl.76.2)
Advertising & Campaign Management
FinTech
Payments & Invoicing

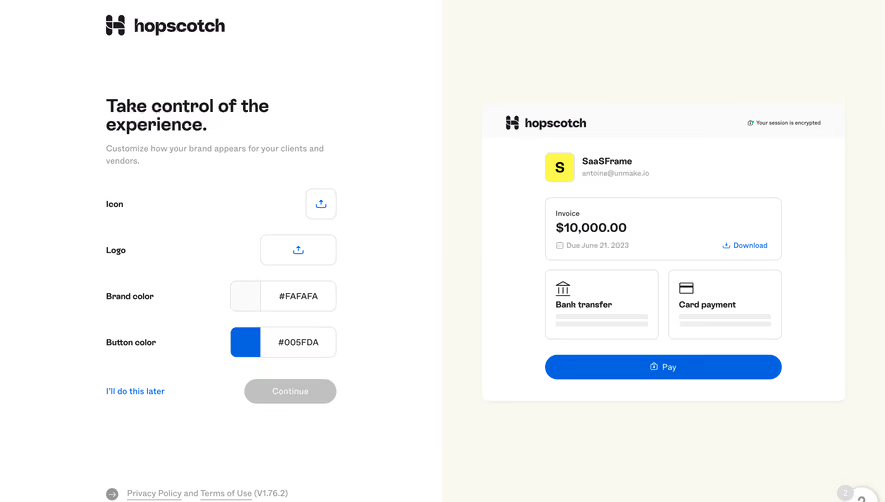
Appearance Customization
Hopscotch
Appearance Customization
Product
hopscotch Take control of the experience. Customize how your brand appears for your clients and vendors. loon Logo Brand color Button color I'll do this later hopscotch SaaSFrame S [email protected] Invoice $10,000.00 Due June 21, 2023 Ill Bank transfer tj Your session is encrypted Download Card payment #FAFAFA #005FDA Continue Pay Privacy Policy and Terms of Use (Vl.76.2)
Advertising & Campaign Management
FinTech
Payments & Invoicing

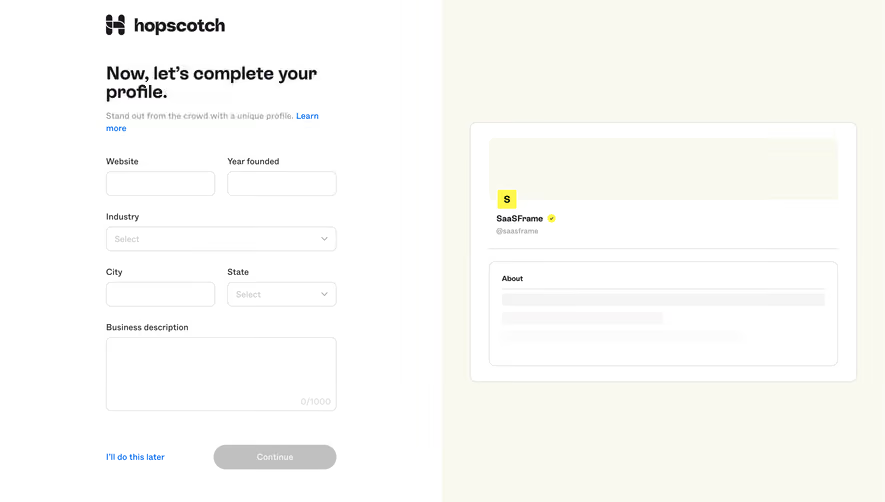
Account Setup
Hopscotch
Account Setup
Product
hopscotch Now, let's complete your profile. Stand out from the crowd with a unique profile. Learn more Website Industry Select City Business description I'll do this later Year founded State Select 0/1000 Continue s SaaSFrame @saasframe About Privacy Policy and Terms of Use (Vl.76.2)
Advertising & Campaign Management
FinTech
Payments & Invoicing

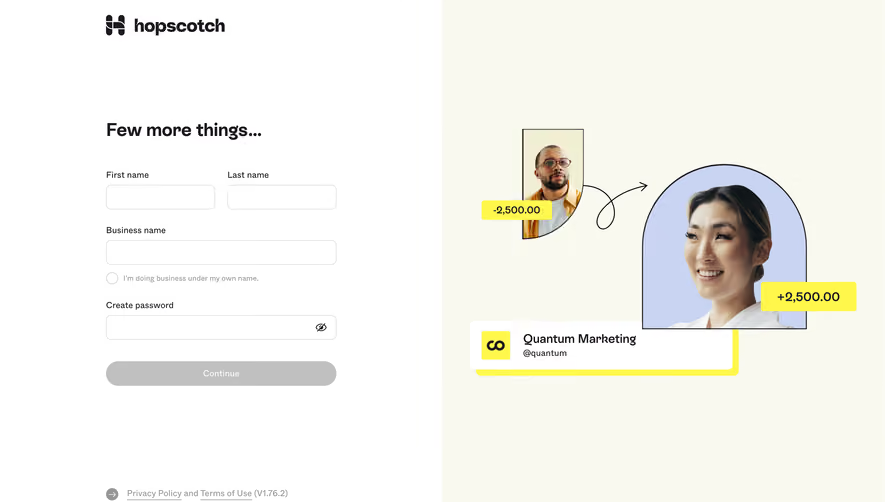
Account Setup
Hopscotch
Account Setup
Product
hopscotch Few more things... First name Business name Last name O I'm doing business under my own name. Create password Continue Privacy Policy and Terms of Use (Vl.76.2) -2,500.00 Quantum Marketing @quantum +2,500.00
Advertising & Campaign Management
FinTech
Payments & Invoicing


Verification
Hopscotch
Verification
Product
hopscotch Check your email To confirm it's really you, we sent a verification code to [email protected]. Resend Verification code Continue Privacy Policy and Terms of Use (VI .76.2) -2,500.00 Quantum Marketing @quantum +2,500.00
Advertising & Campaign Management
FinTech
Payments & Invoicing


Signup
Hopscotch
Signup
Product
hopscotch Jump into Hopscotch Already a Hopscotcher? Sign in Email Continue By continuing you agree to our Privacy Policy and Terms of Use Privacy Policy and Terms of Use (Vl.76.2) -2,500.00 Quantum Marketing @quantum +2,500.00
Advertising & Campaign Management
FinTech
Payments & Invoicing


Twitter Account Connected
Assembly
Integrations
Product
Settings INTEGRATIONS Slack SCHEDULING Twitter LinkedIn Discord SETTINGS & Members O Notifications Plans x Twitter Integration About the Twitter Integration Connect your Twitter to enable automatic embedded previews of Tweets, view analytics from your tweets, and schedule tweets Antoine Milkoff @amilkoff + Connect another account You will need to switch to the account you want to connect on Twitter first. You can do so here
Advertising & Campaign Management
Marketing Automation


Connect Twitter
Assembly
Integrations
Product
Settings INTEGRATIONS Slack SCHEDULING Twitter LinkedIn Discord SETTINGS & Members O Notifications Plans x Twitter Integration About the Twitter Integration Connect your Twitter to enable automatic embedded previews of Tweets, view analytics from your tweets, and schedule tweets CONNECT TWITTER
Advertising & Campaign Management
Marketing Automation


Empty Inbox
Assembly
Inbox
Product
Assembly Q Search... NOTIFICATIONS Inbox Approvals POSTS SA Notifications All an as + Assembly A1 BETA All Posts SAVED FILTERS No saved filters SETTINGS O Help & Invite to Assembly @ Integrations Logout No notifications yet We'll let you know when we've got something new for you. No Unread Notifications Click here to customize what notifications you'd like to receive from Assembly
Advertising & Campaign Management
Marketing Automation


Create A Post
Assembly
Add & Edit
Product
Assembly Inbox Approvals + Assembly A1 All Posts O Help & Invite to Assembly @ Integrations Logout June 12 19 JUNET Filter Today 13 Enter Post STATUS * TO DO POST DATE* 6/18/2023 You currently have 14 days remaining in your trial. 15 Title Upgrade Now. 16 CHANNEL * TWITTER POST TIME (OPTIONAL) CAMPAIGN (OPTIONAL) + CAMPAIGN Marketers Hide Campaigns 17 x CREATE POST | 2 Weeks I 18 FATHER'S DAY 25 Assembly: Start her... Feature
Advertising & Campaign Management
Marketing Automation


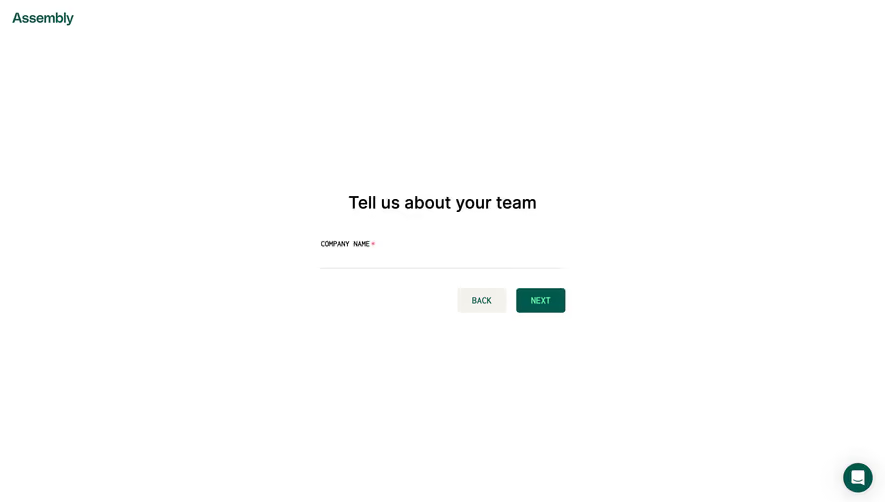
Account Setup
Assembly
Account Setup
Product
Assembly Tell us about your team COMPANY NAME* BACK NEXT
Advertising & Campaign Management
Marketing Automation


Account Setup
Assembly
Account Setup
Product
Assembly Hi there, what should we call you? FIRST NAME* LAST NAME* NEXT
Advertising & Campaign Management
Marketing Automation


Verification
Assembly
Verification
Product
Assembly Already have an account? Check your Email We've sent a temporary login link to [email protected] You can also enter your login code manually below. Enter the Login Code CONTINUE WITH LOGIN CODE LOGIN
Advertising & Campaign Management
Marketing Automation


Signup
Assembly
Signup
Product
Assembly Sign Up for Assembly Continue with Google OR Enter your Email Address CONTINUE WITH EMAIL Already have an account? LOGIN
Advertising & Campaign Management
Marketing Automation








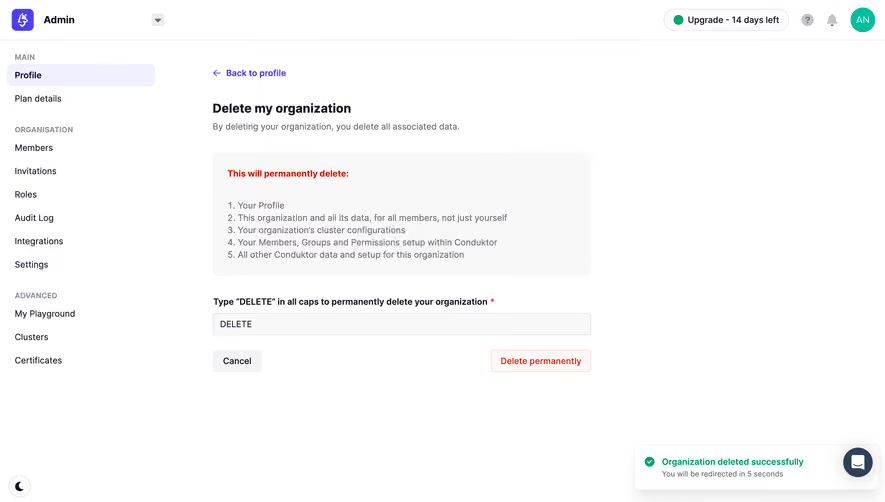


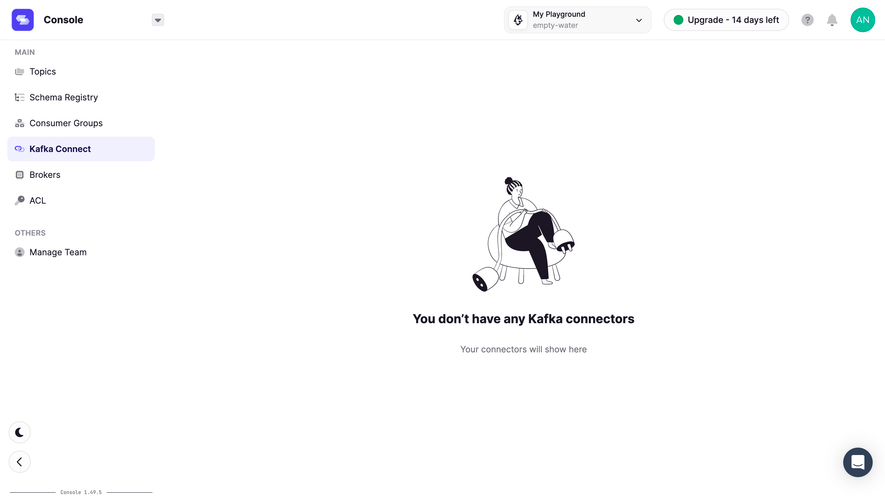
Empty State
Conduktor
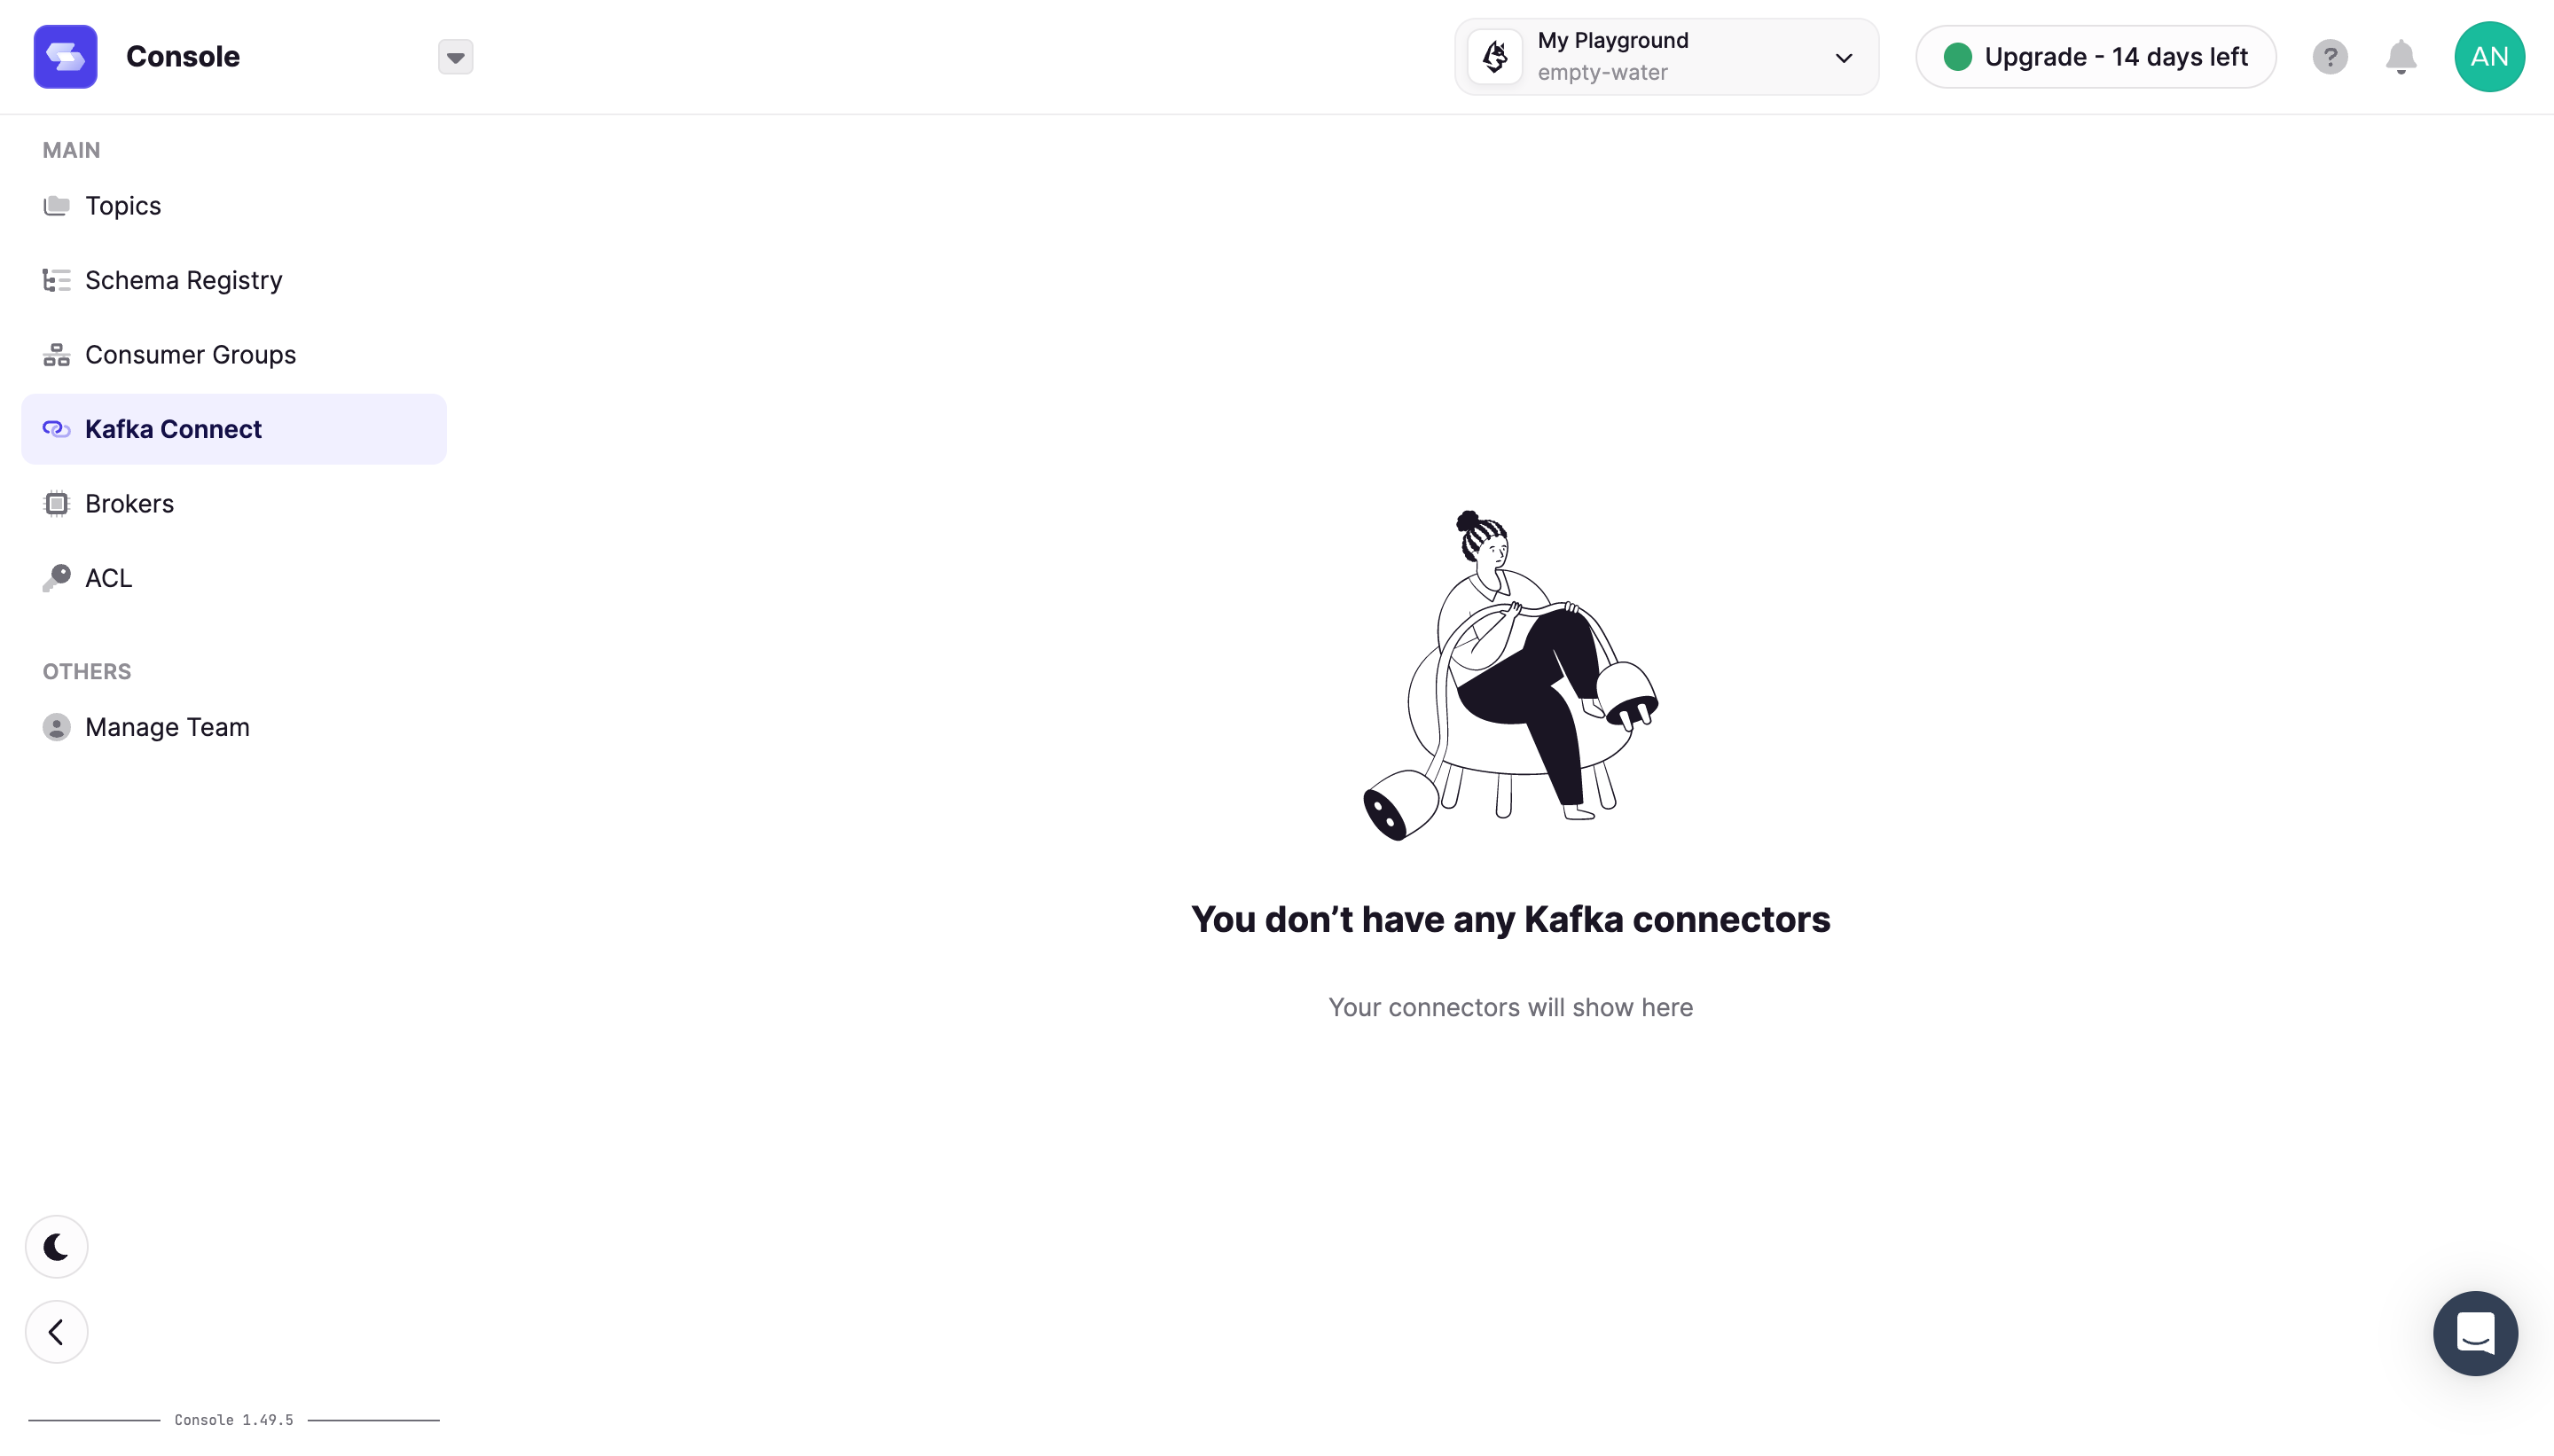
Empty State
Product
Console MAIN My Playground empty-water You don't have any Kafka connectors Your connectors will show here Upgrade - 14 days left AN O) O 0 Topics Schema Registry Consumer Groups Kafka Connect Brokers ACL OTHERS Manage Team Console 1.49.5
API Management
Observability & Monitoring
Empty State
Conduktor
Empty State
Product
Console MAIN My Playground empty-water Upgrade - 14 days left AN O 0 Topics Schema Registry Consumer Groups Kafka Connect Brokers ACL OTHERS Manage Team Console 1.49.5 o You don't have any topics in this cluster Let's get you started by creating your first topic + Create topic
API Management
Observability & Monitoring



Empty
Conduktor
Empty
Product
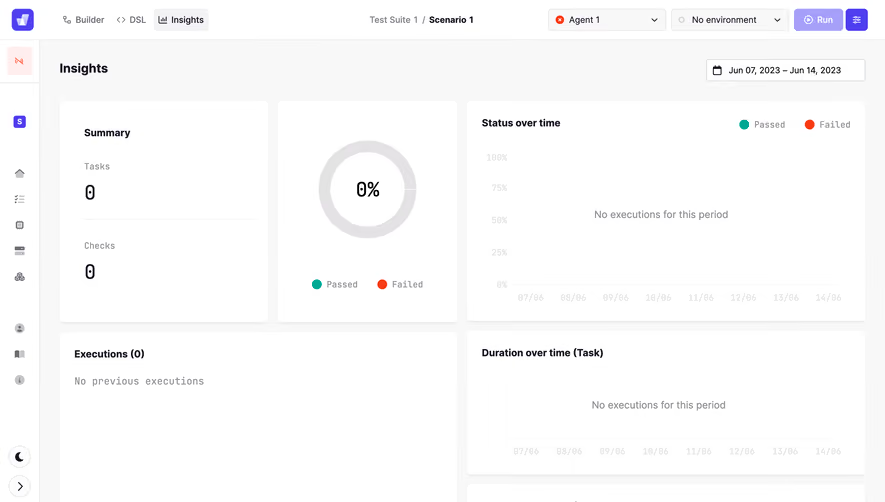
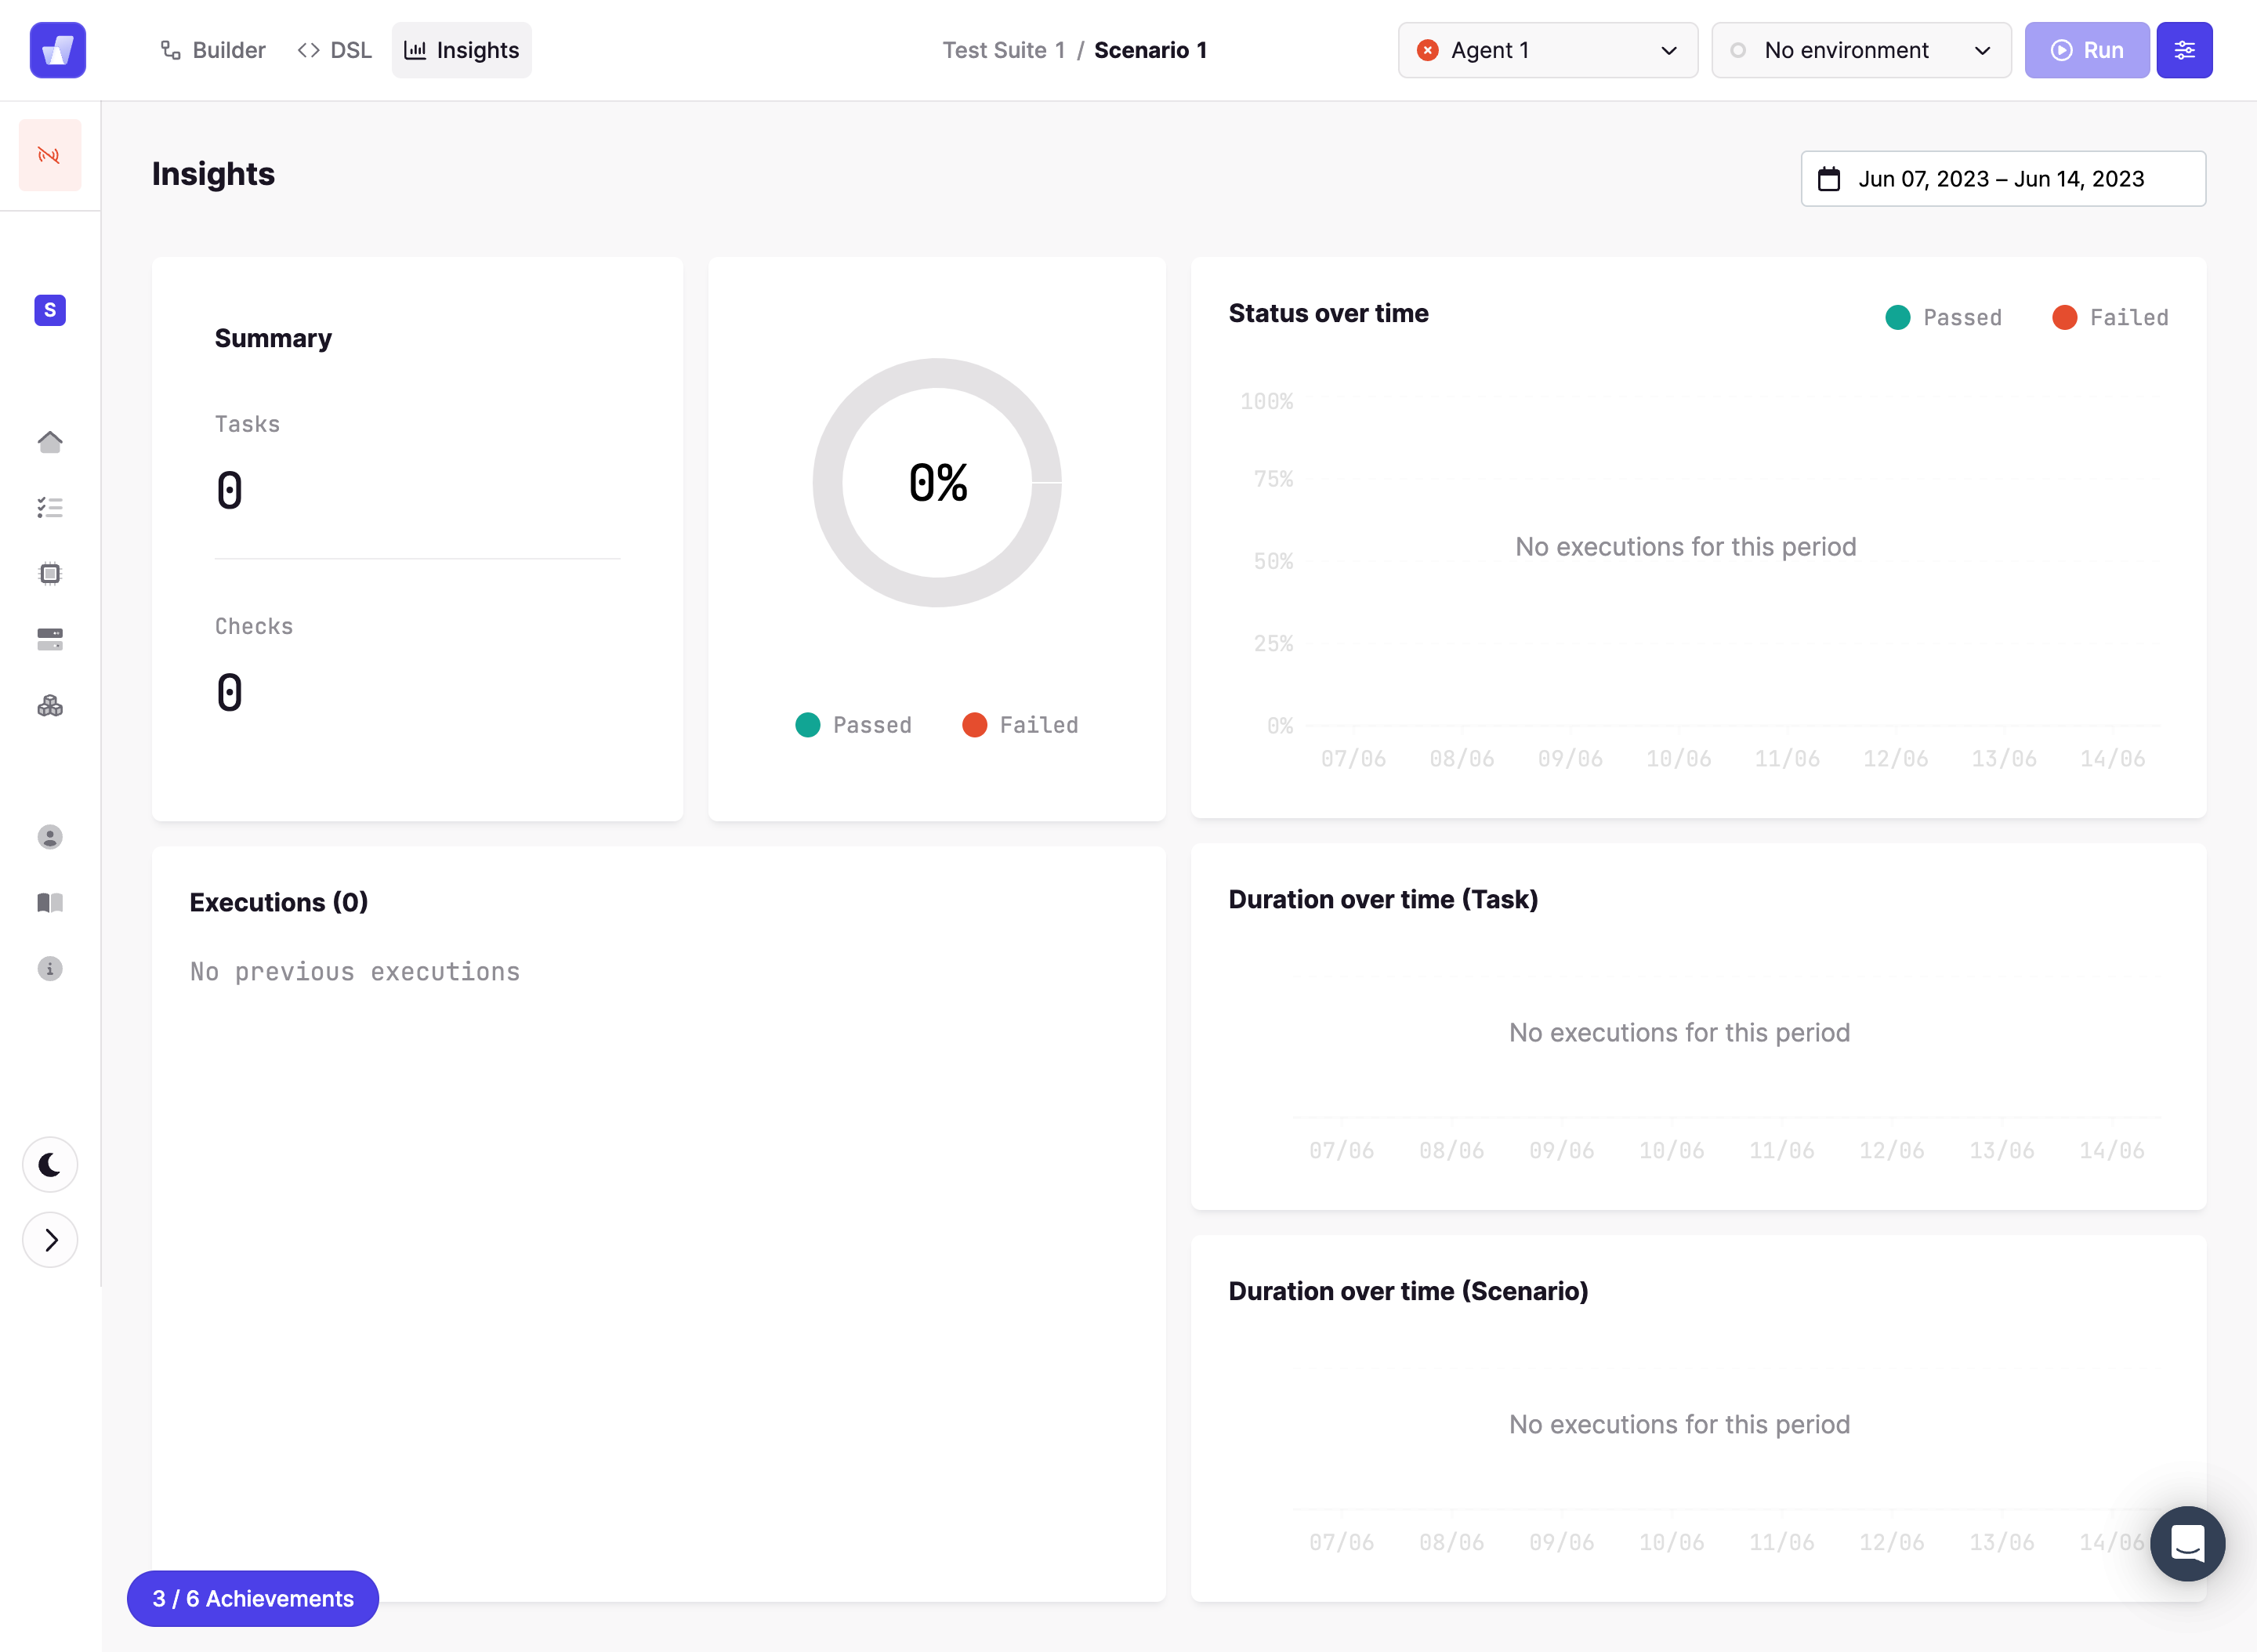
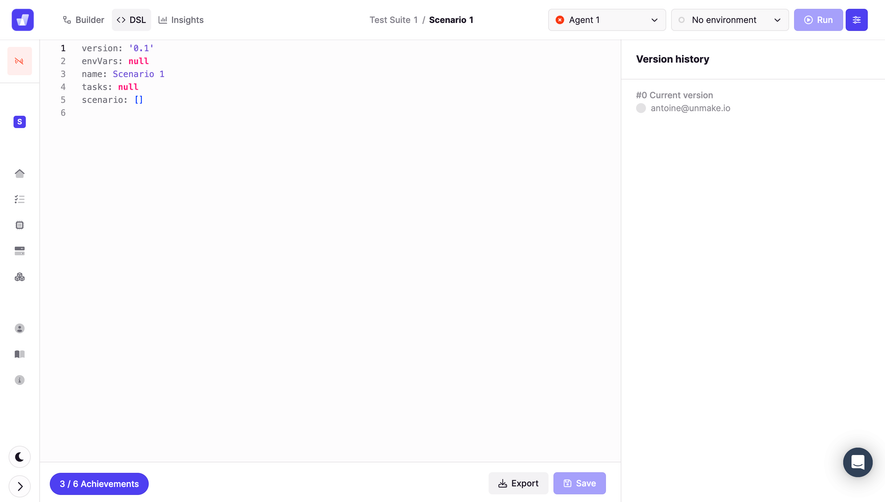
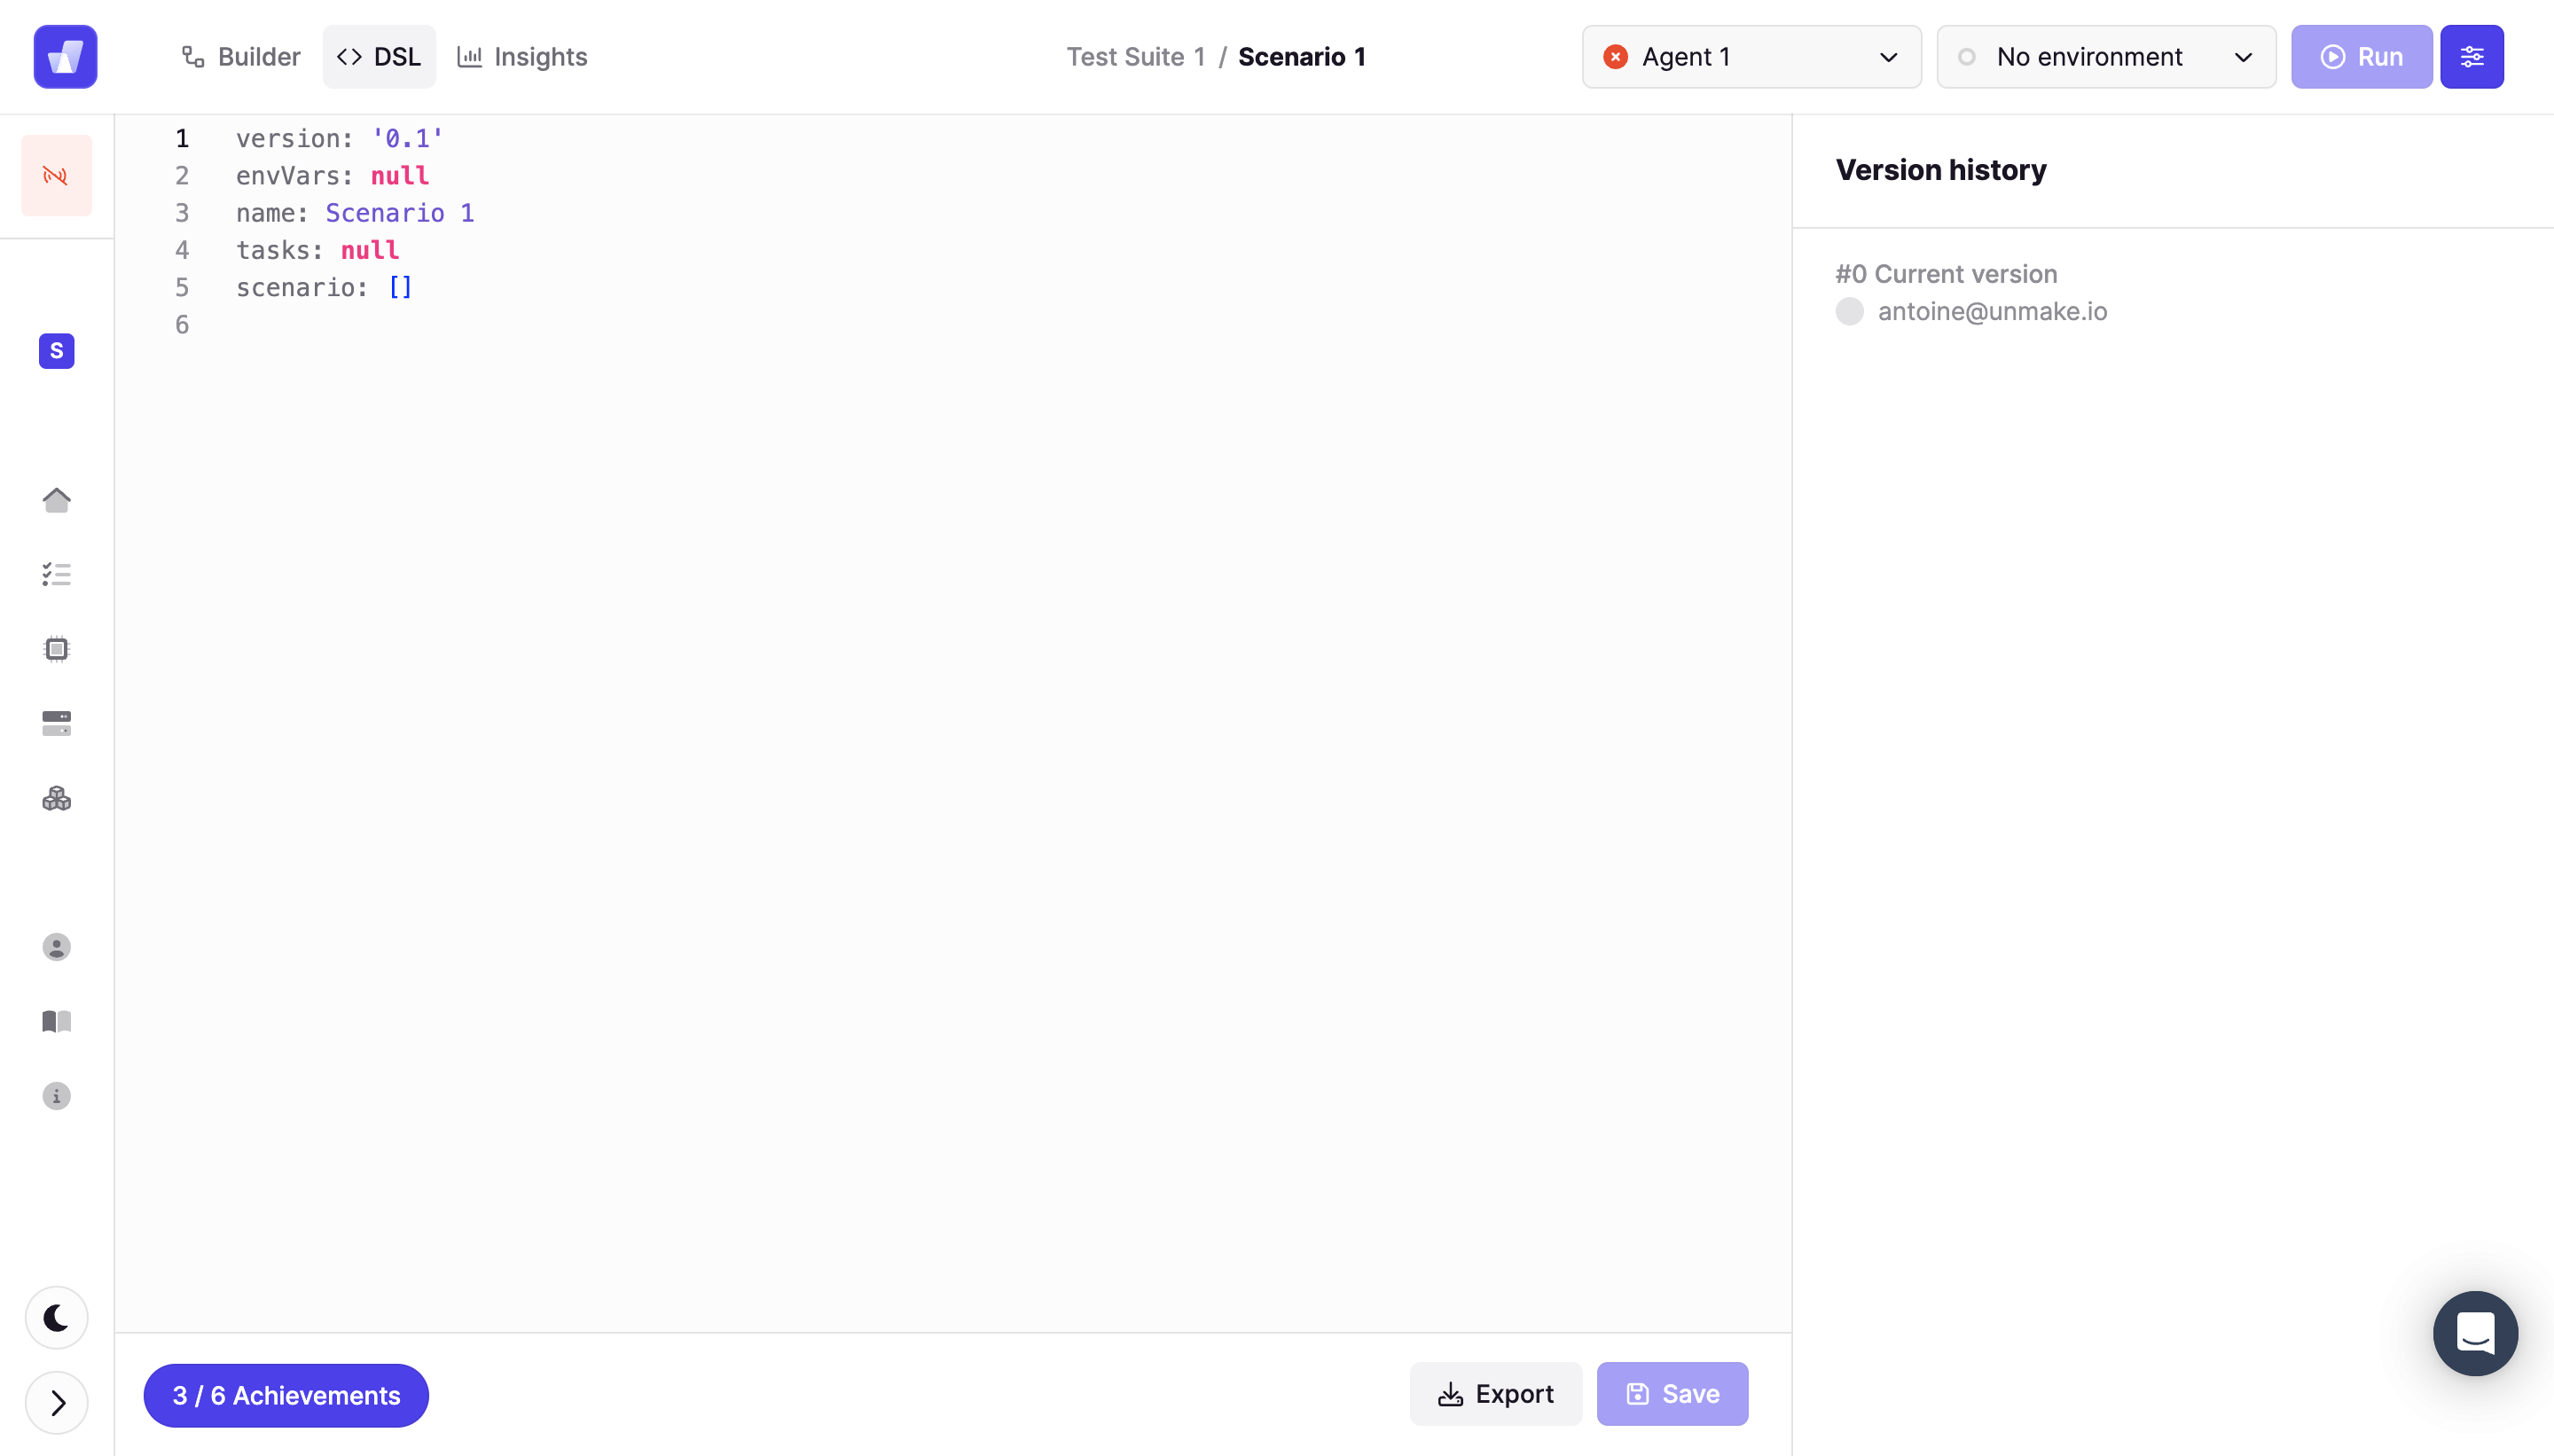
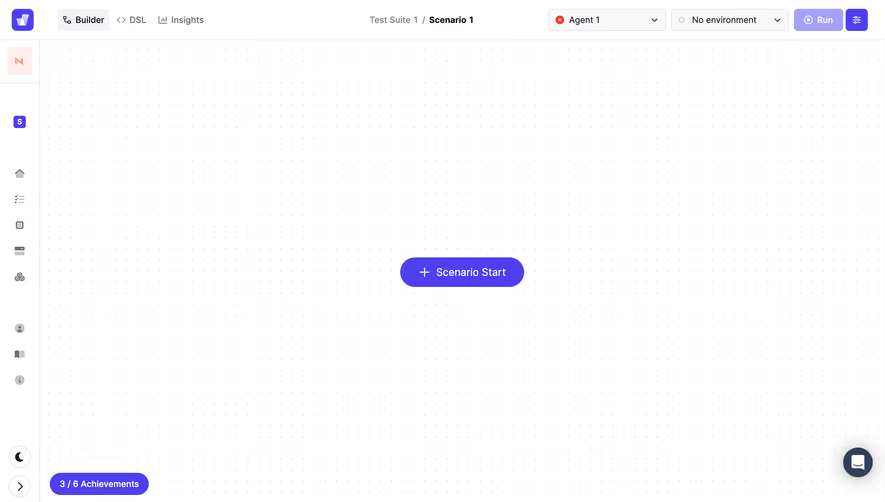
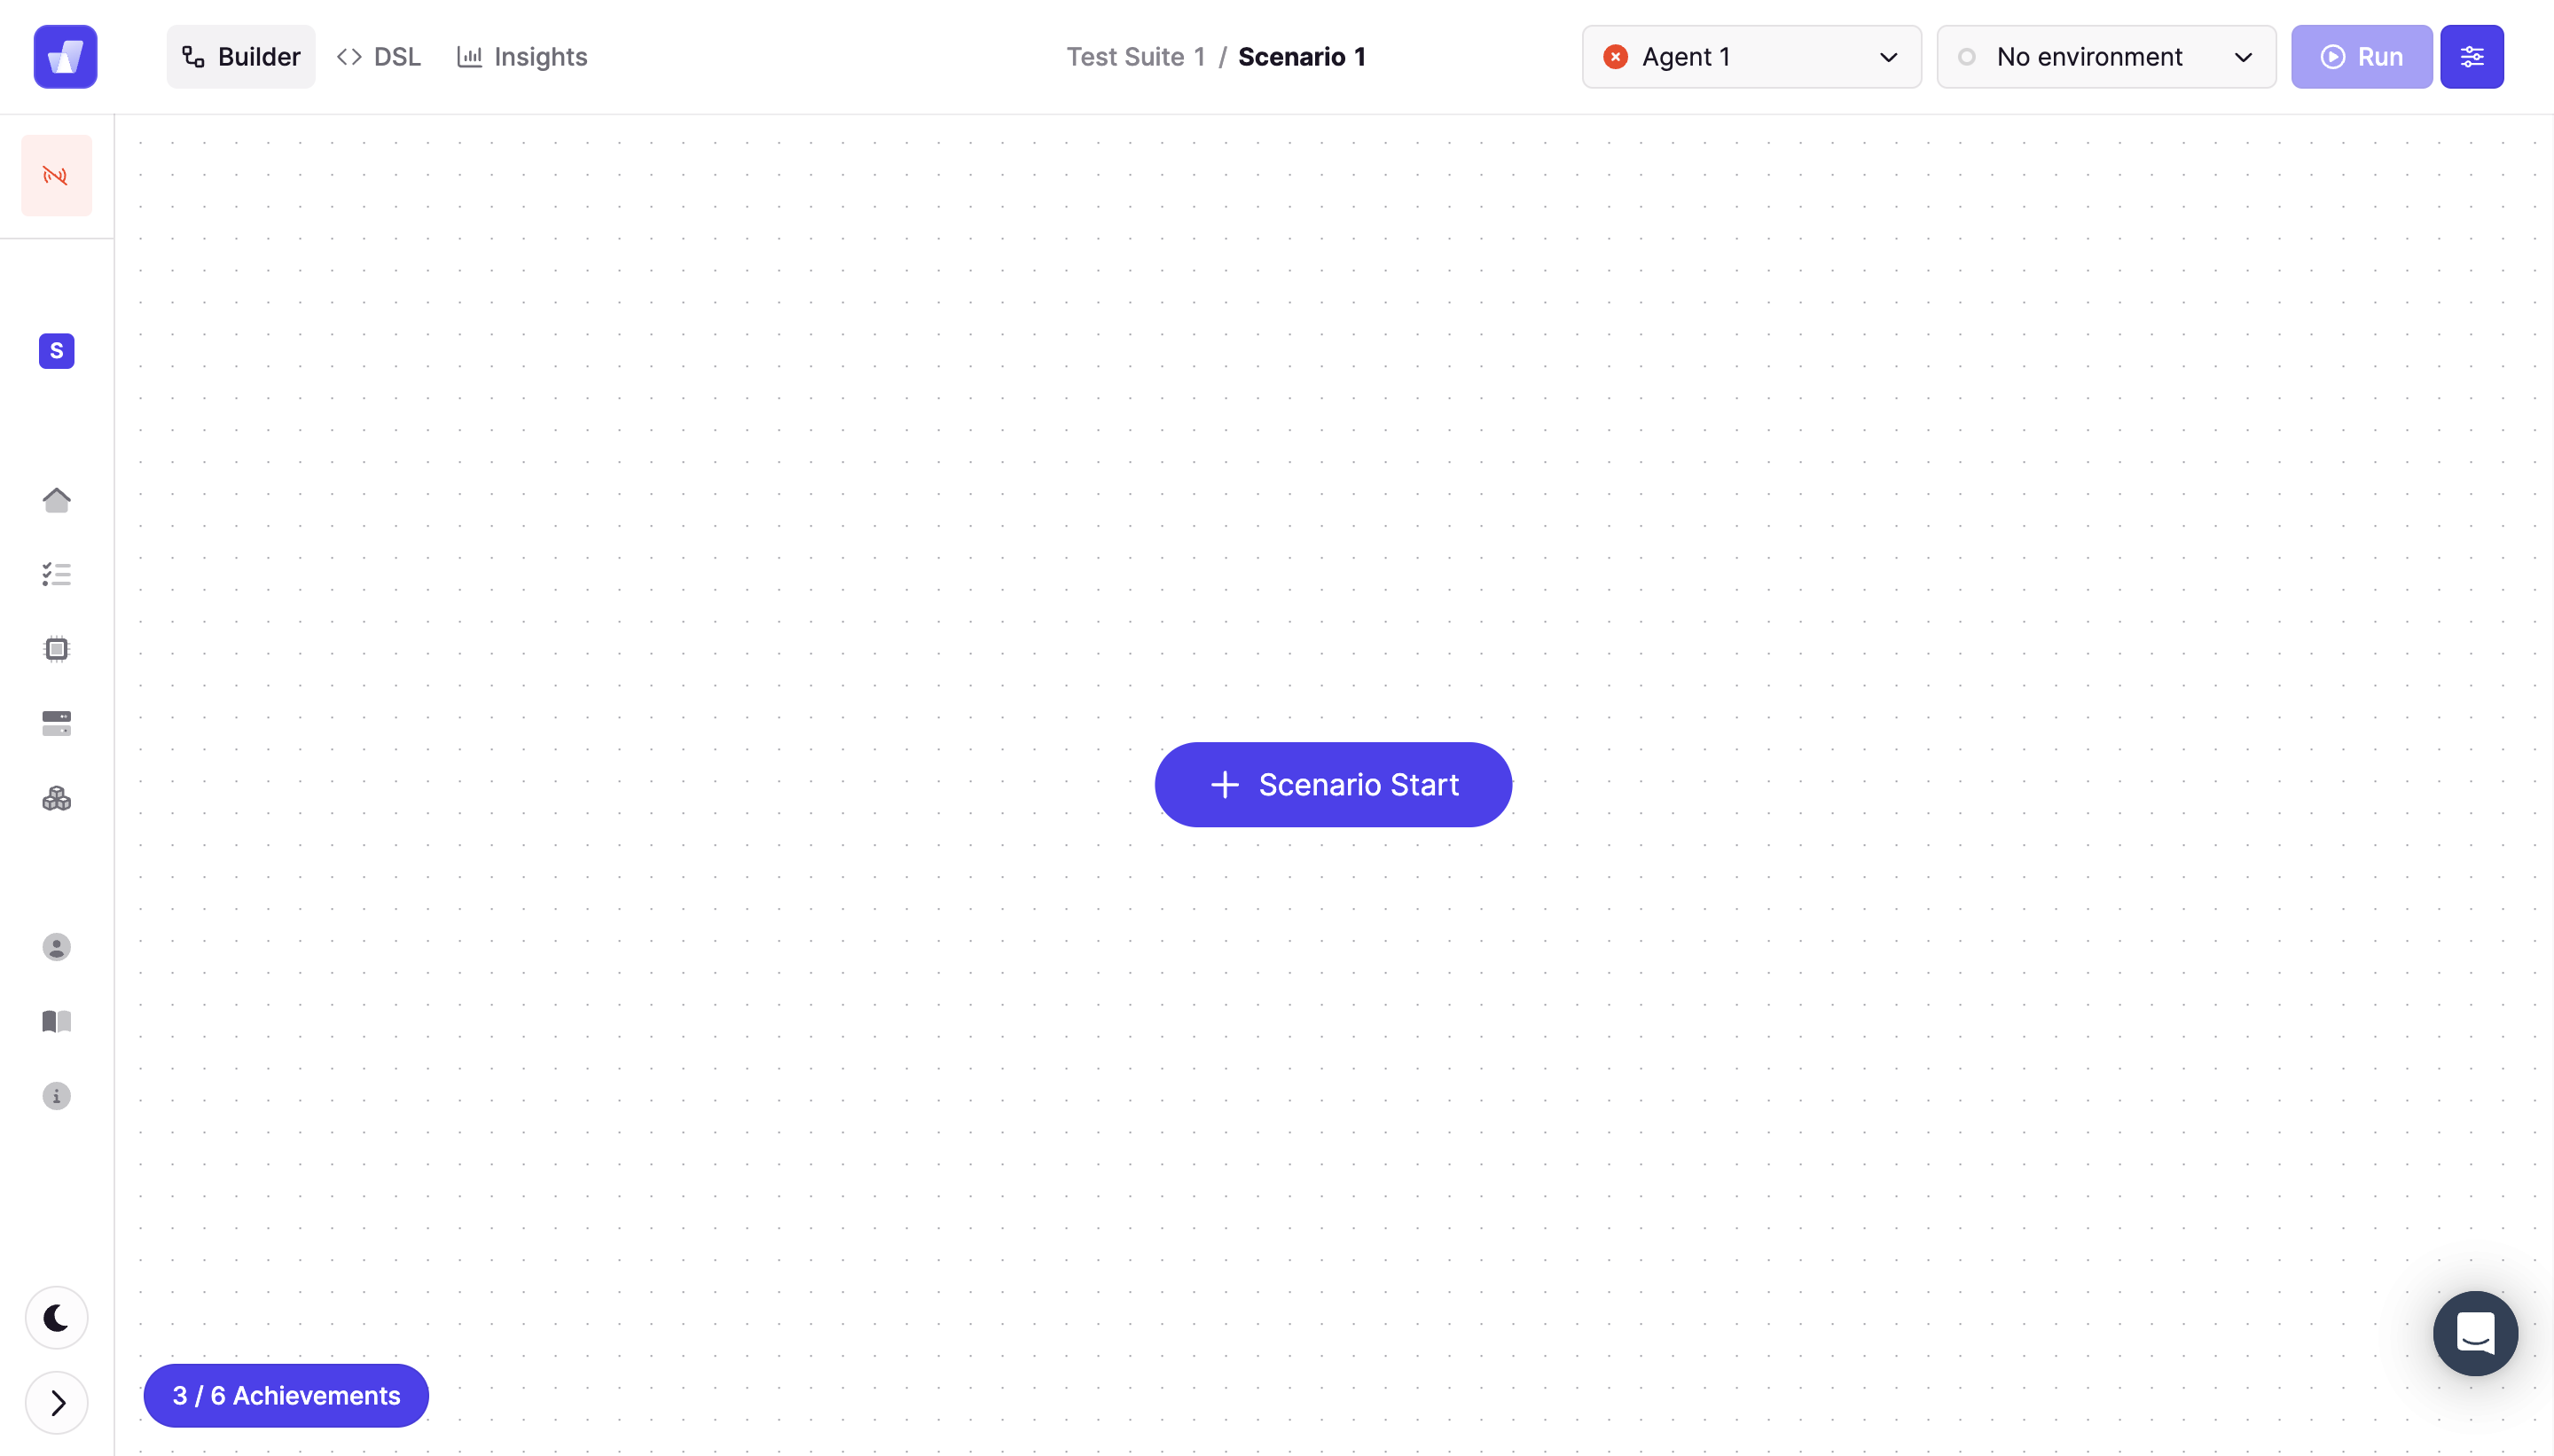
Insights 1 2 3 4 5 6 Builder < > DSL version. • 10.11 null envVars: name: Scenario 1 tasks: nutt scenario: [ ] Test Suite o > Scenario 1 Export O Agent 1 Save o No environment Version history #0 Current version [email protected] 3 / 6 Achievements
API Management
Observability & Monitoring




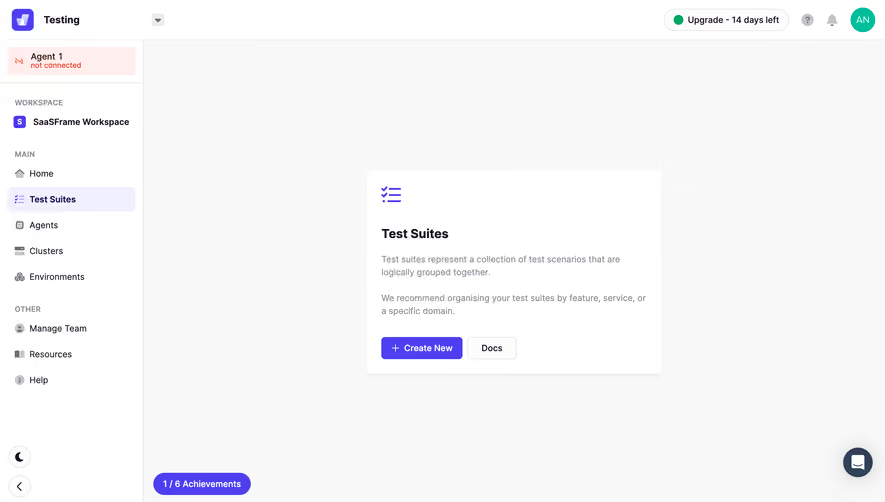
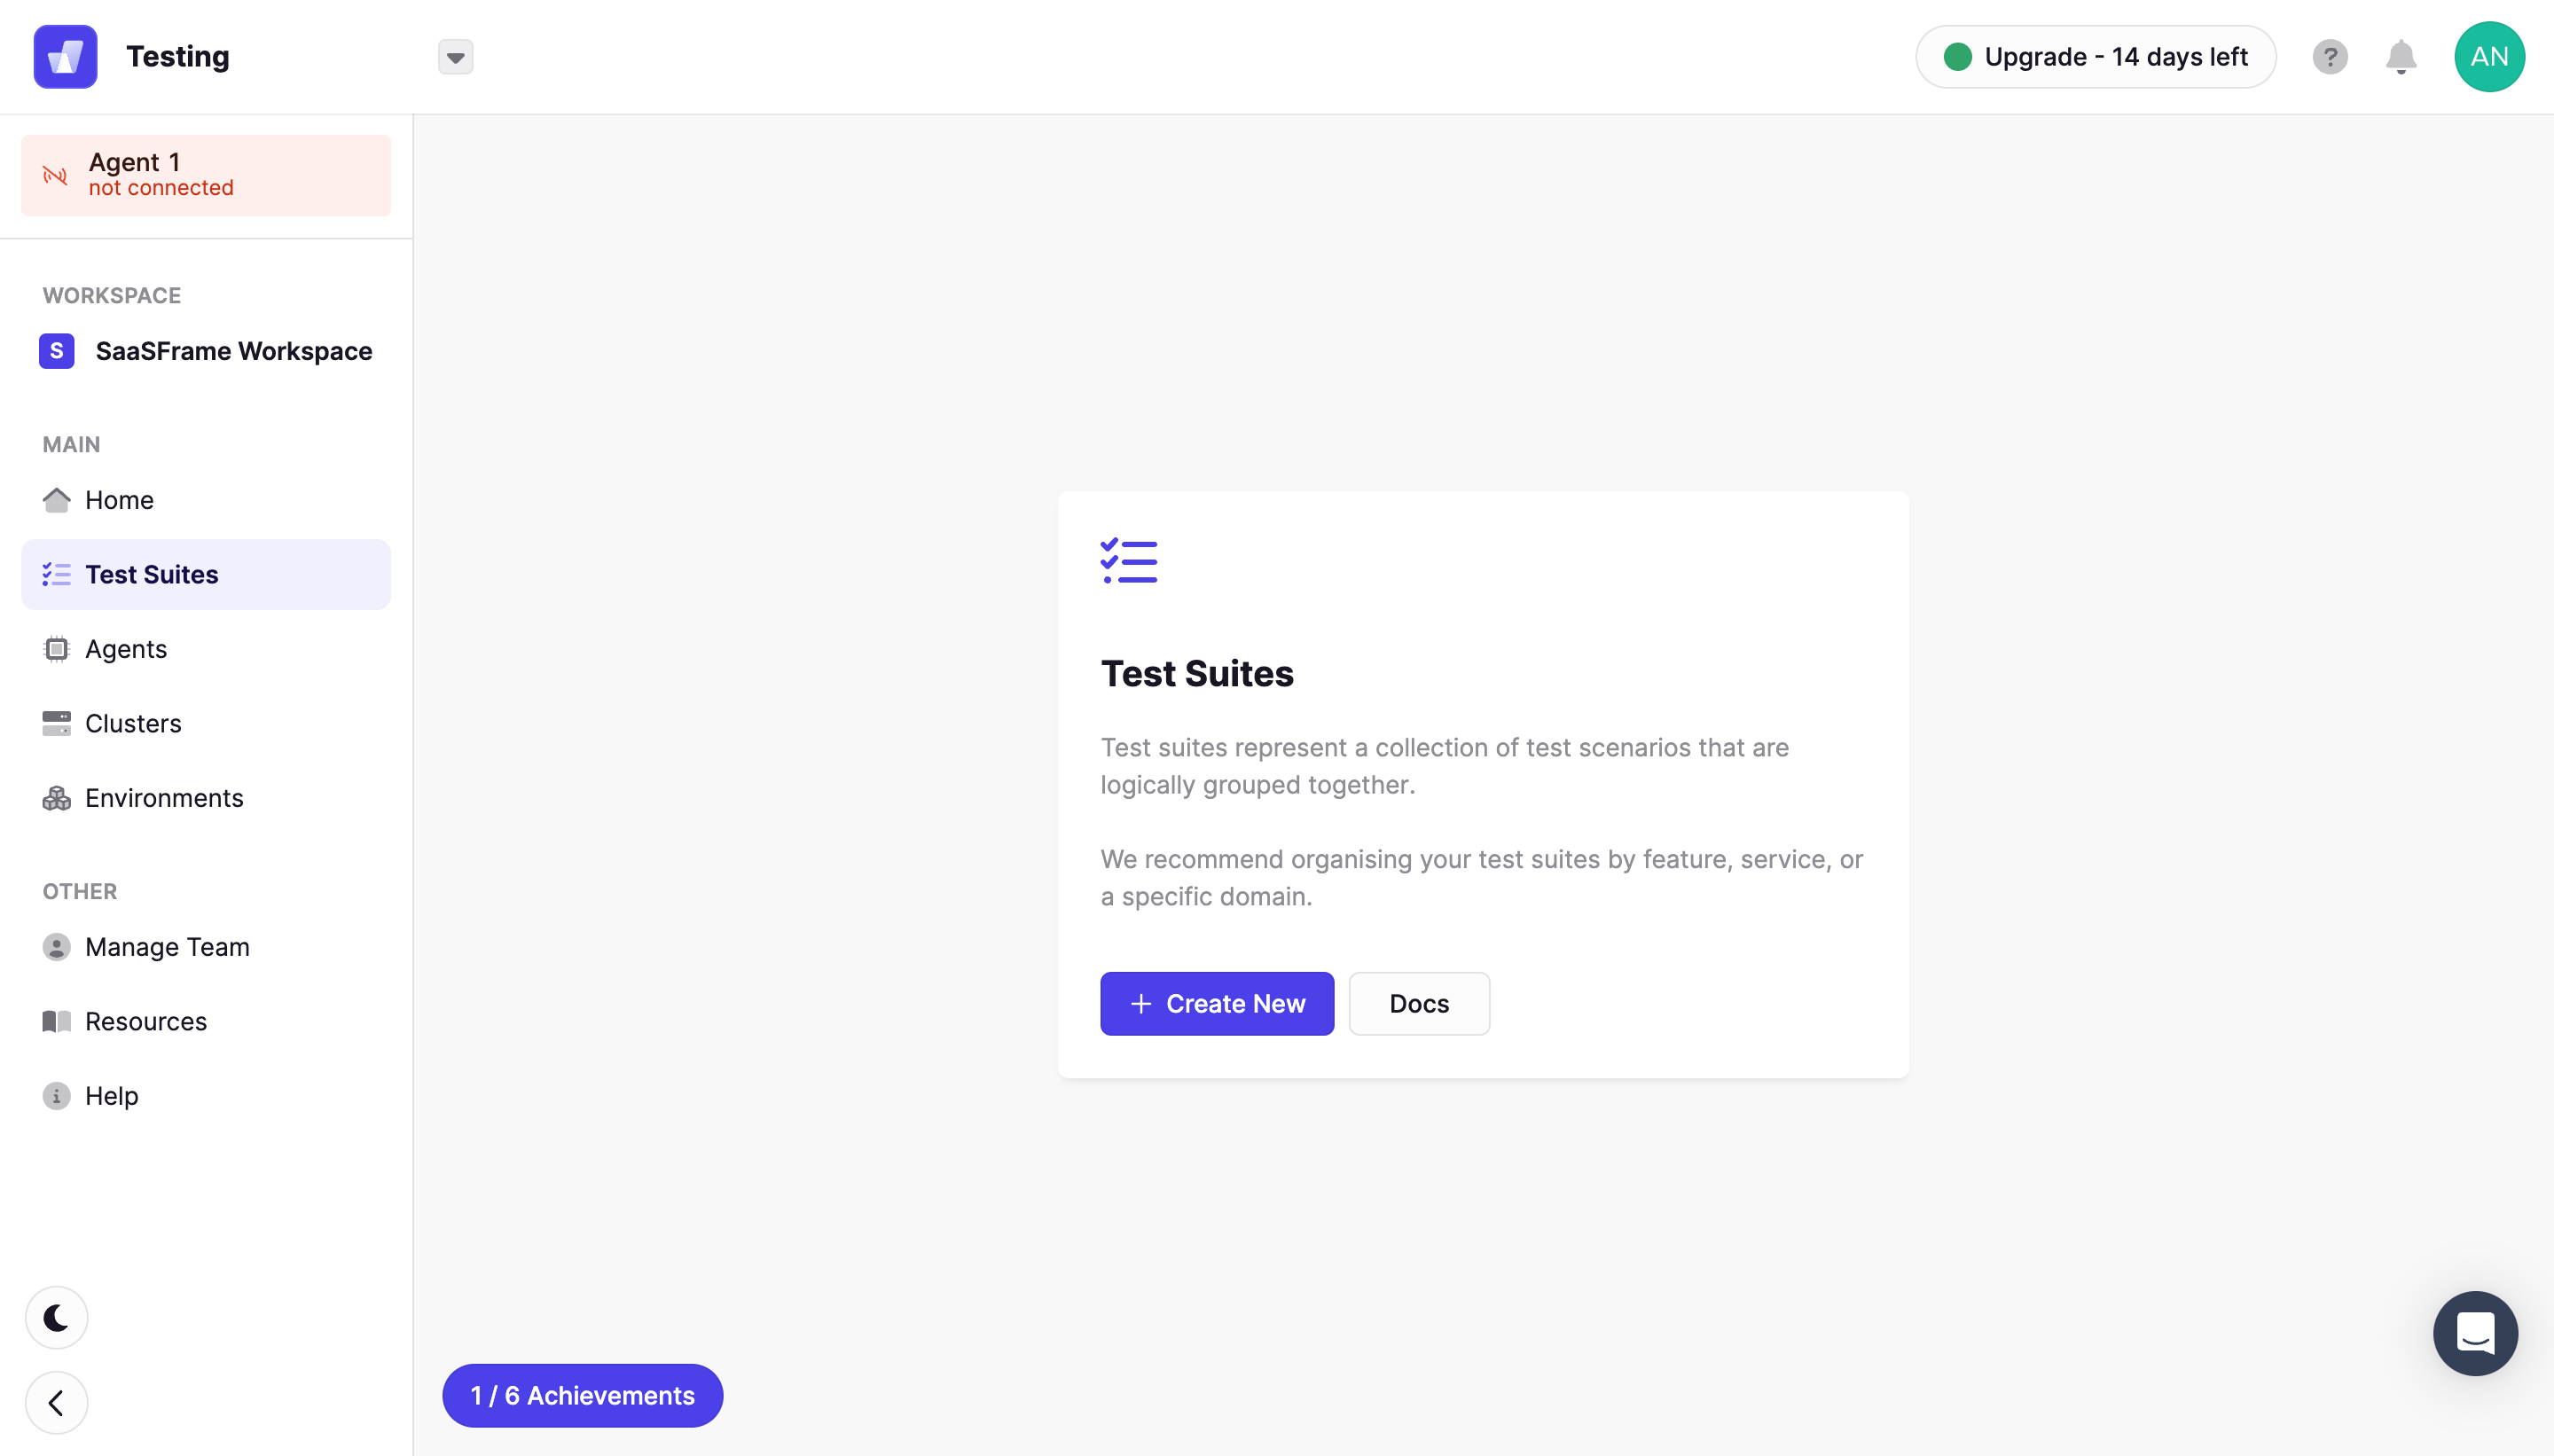
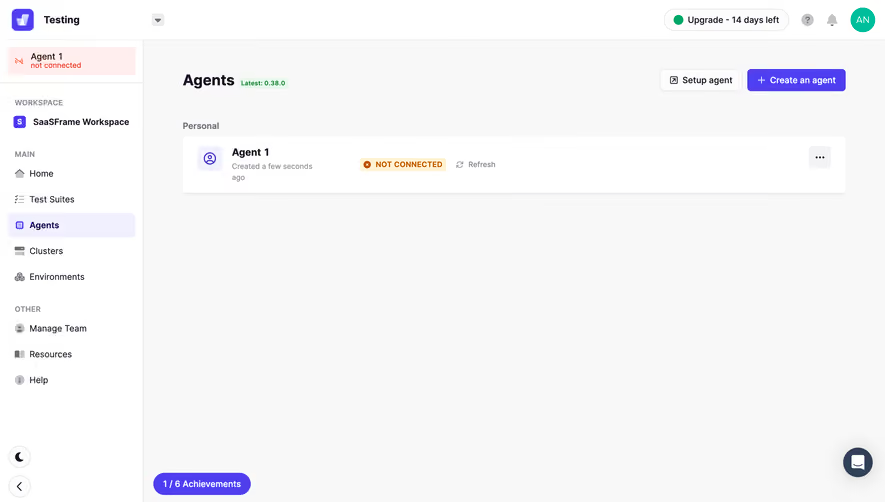
Dashboard
Conduktor
Dashboard
Product
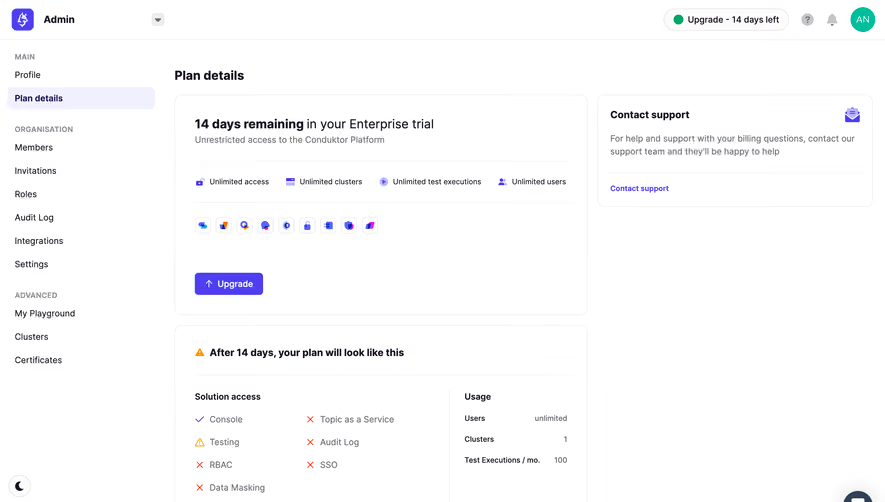
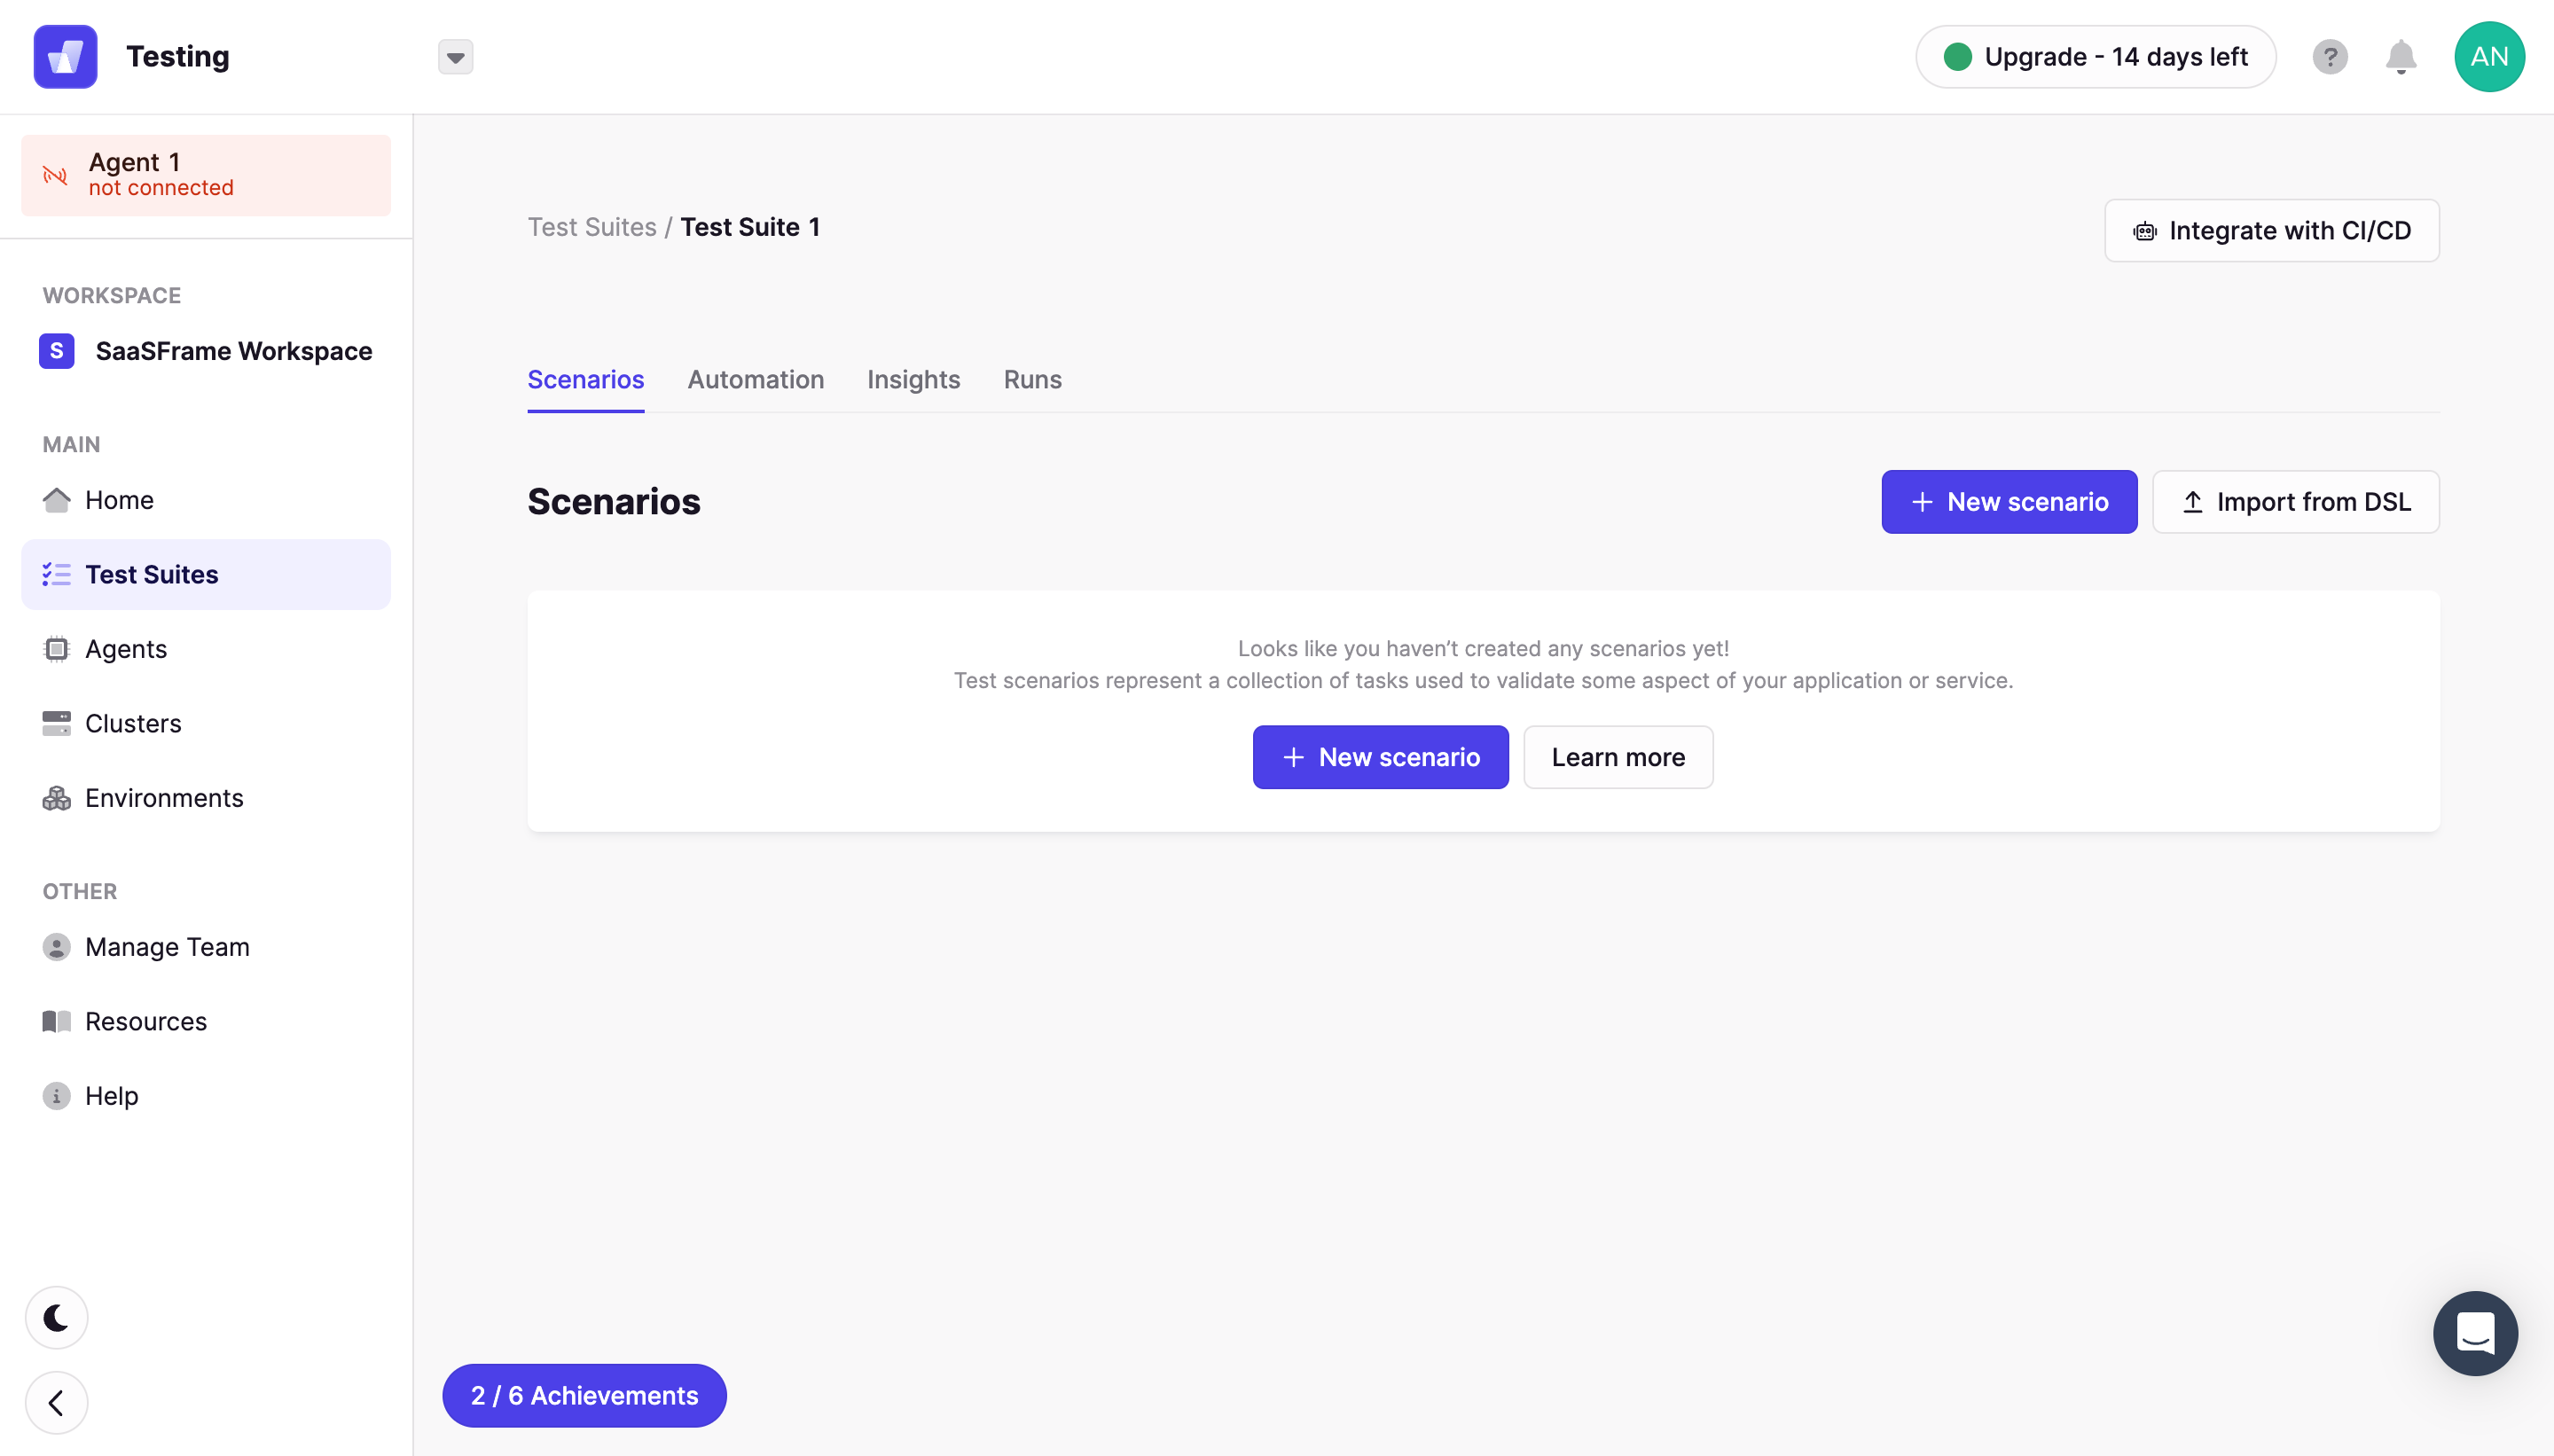
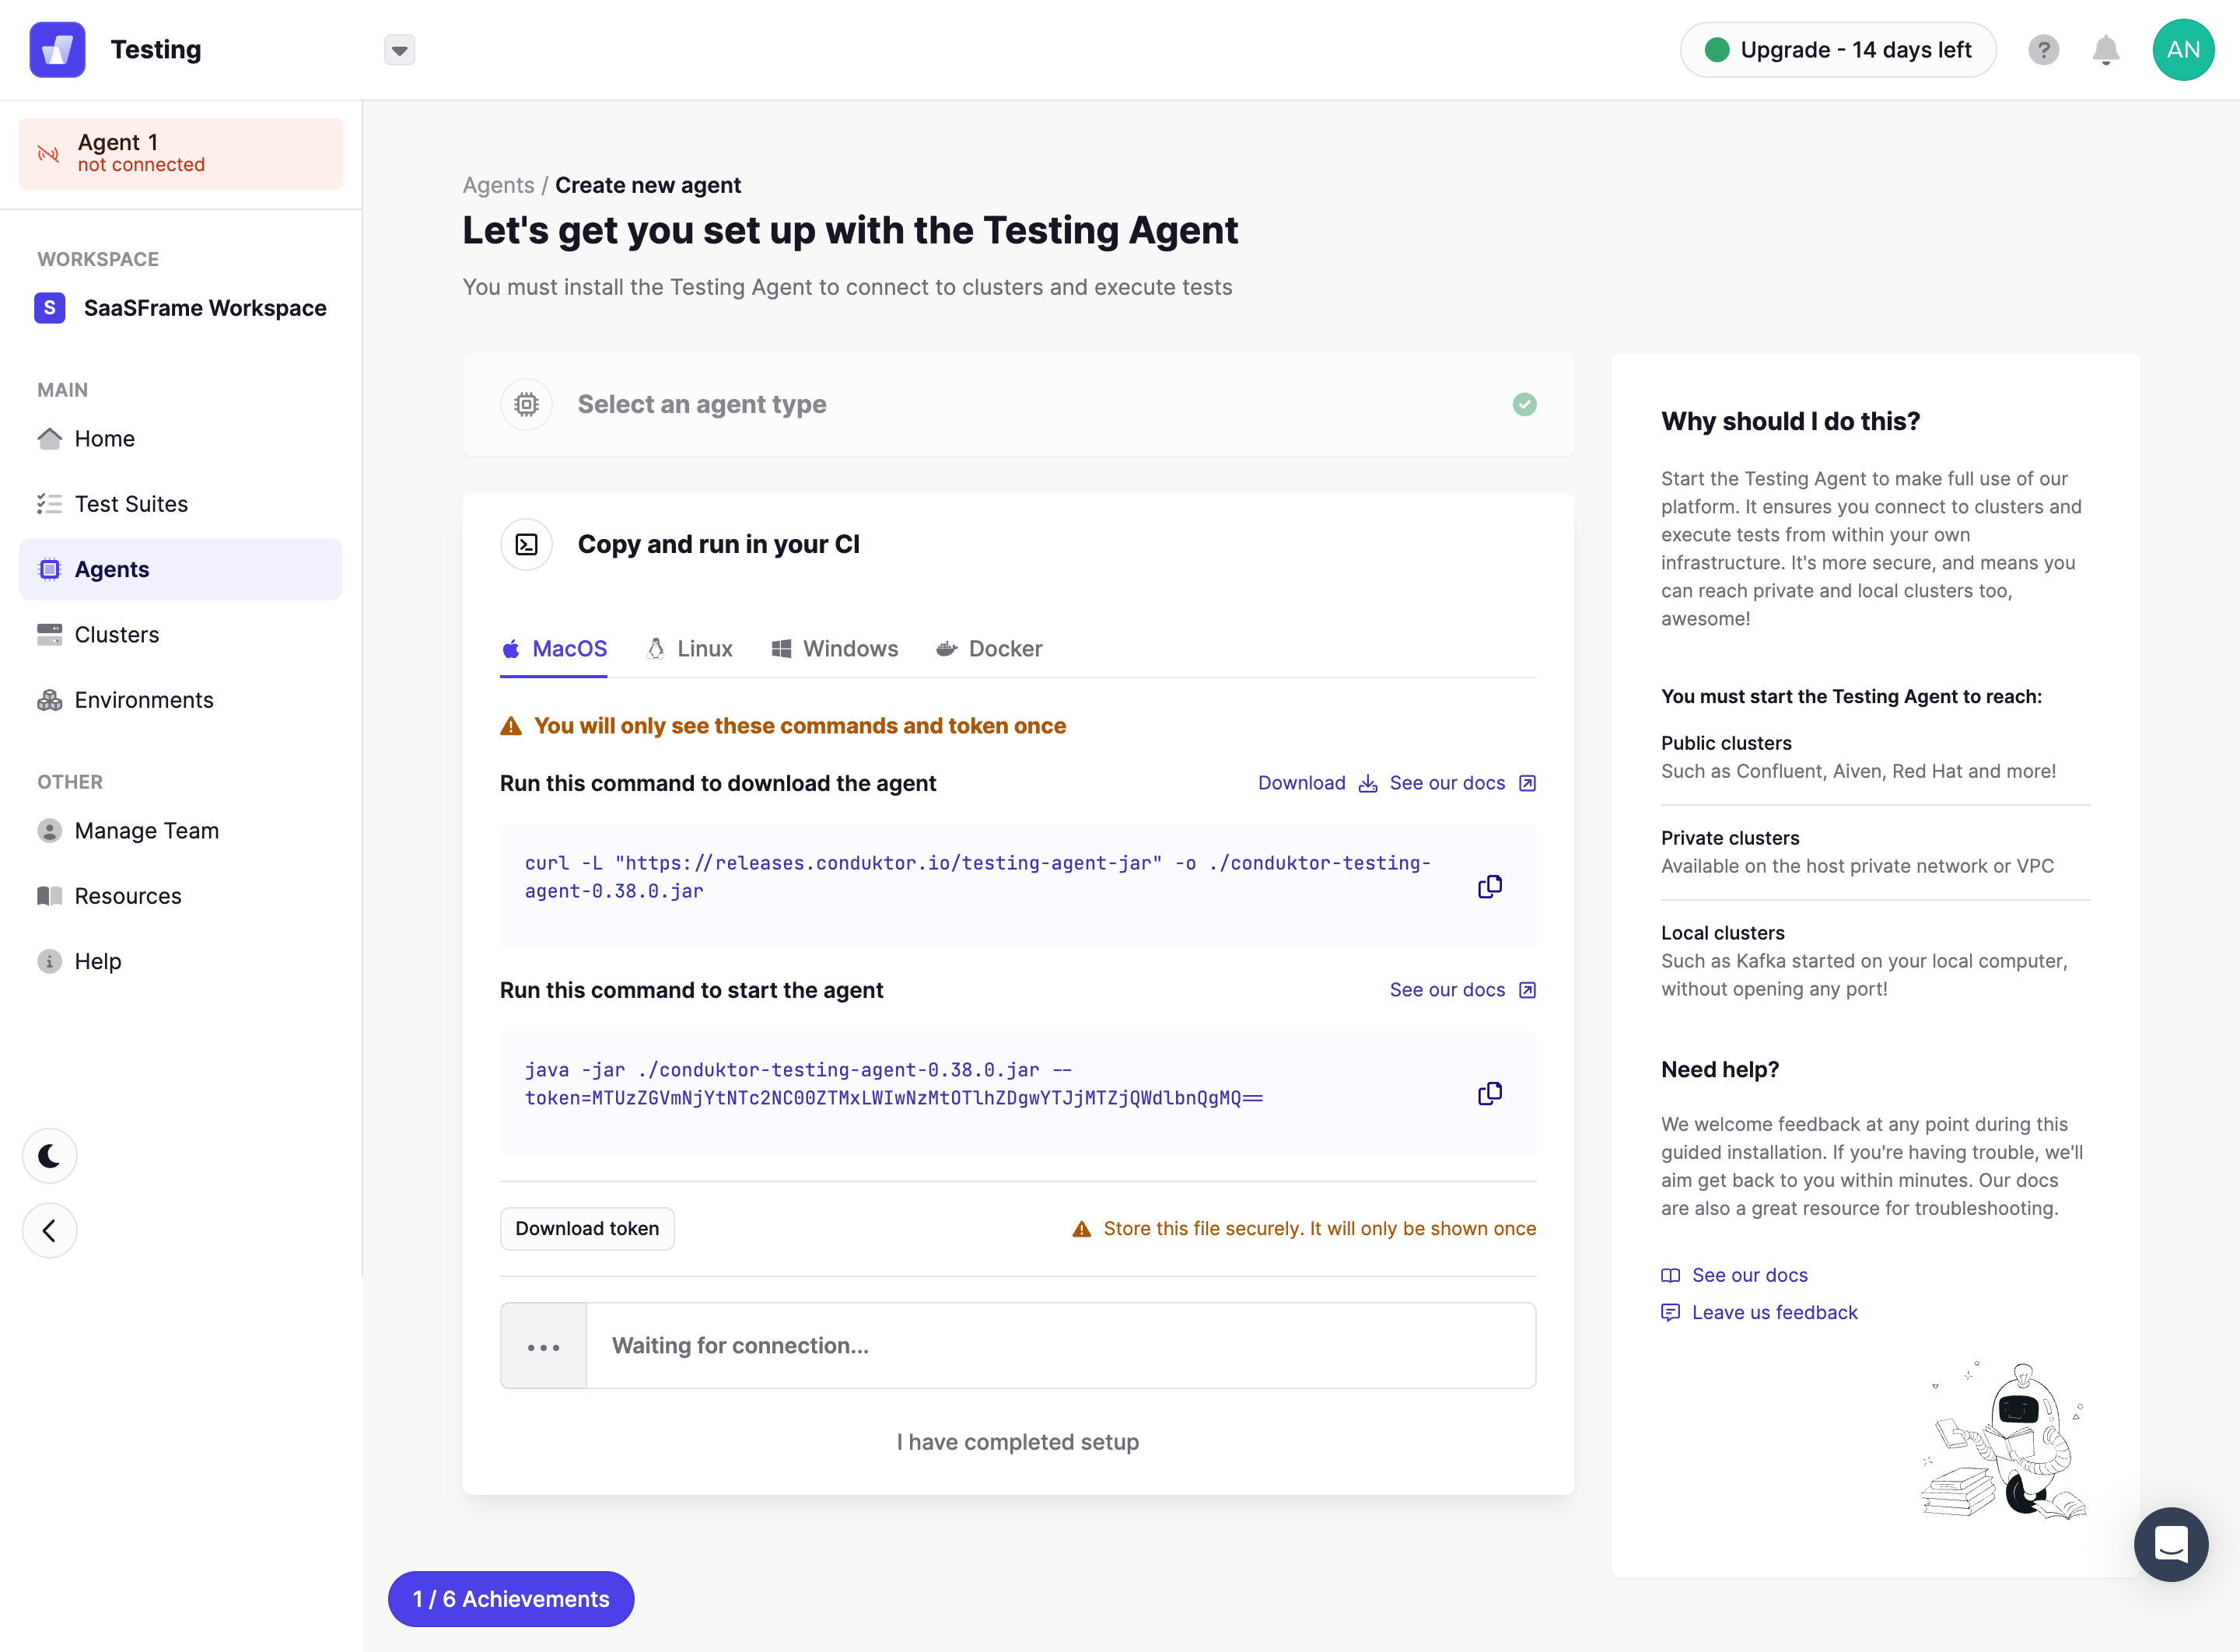
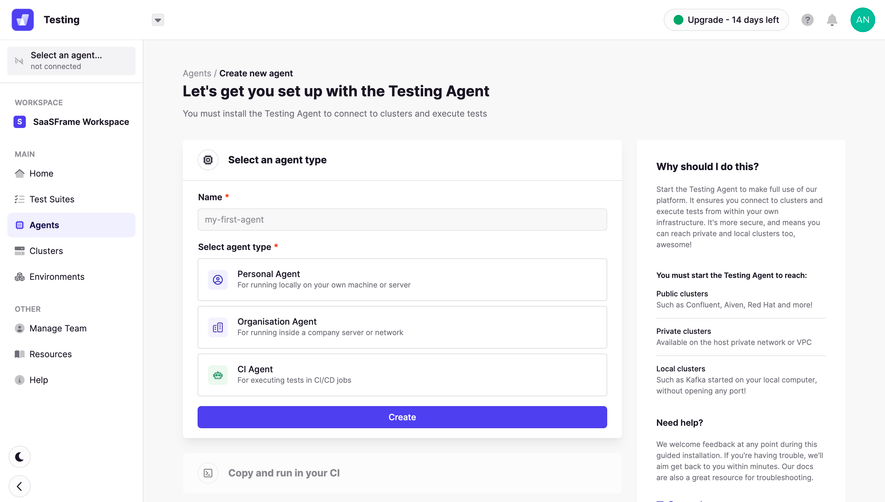
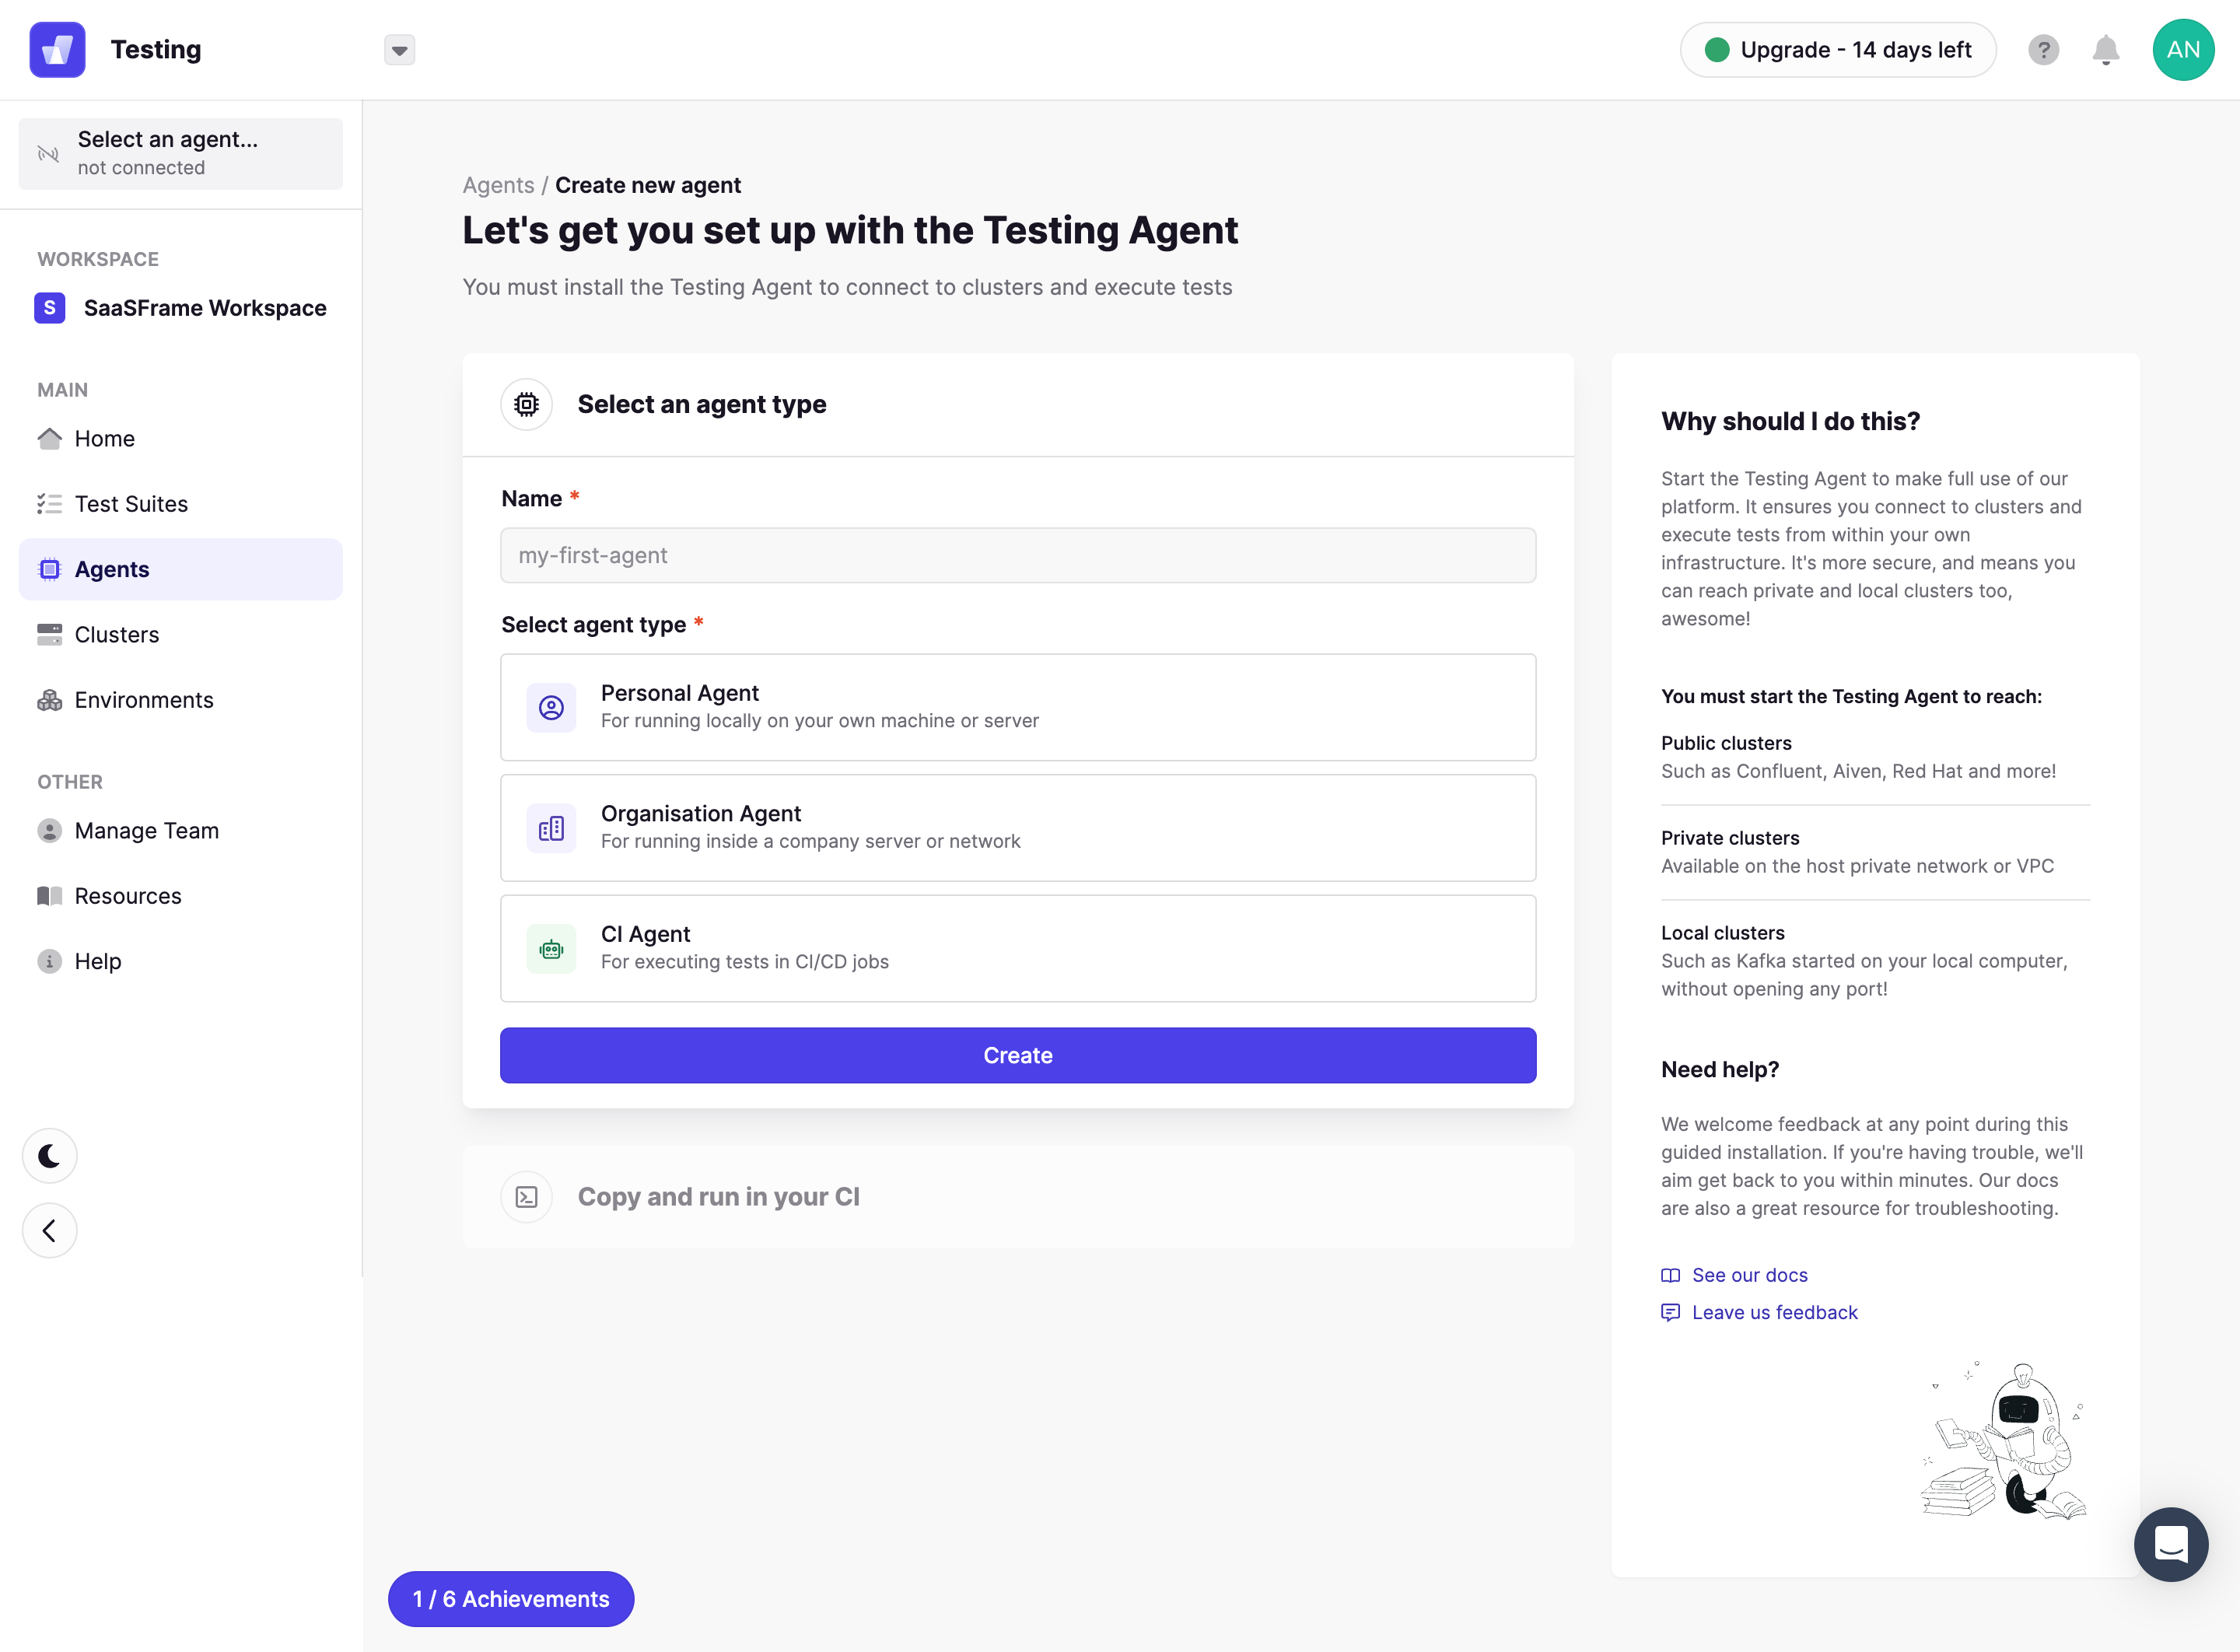
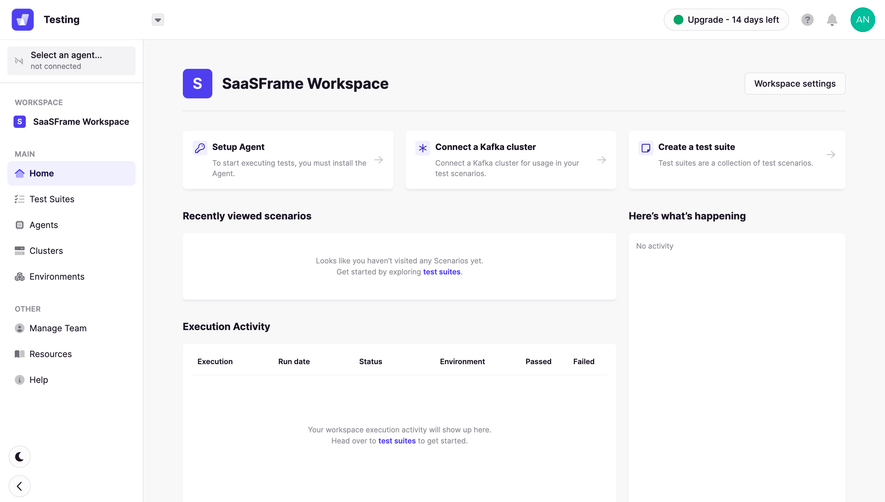
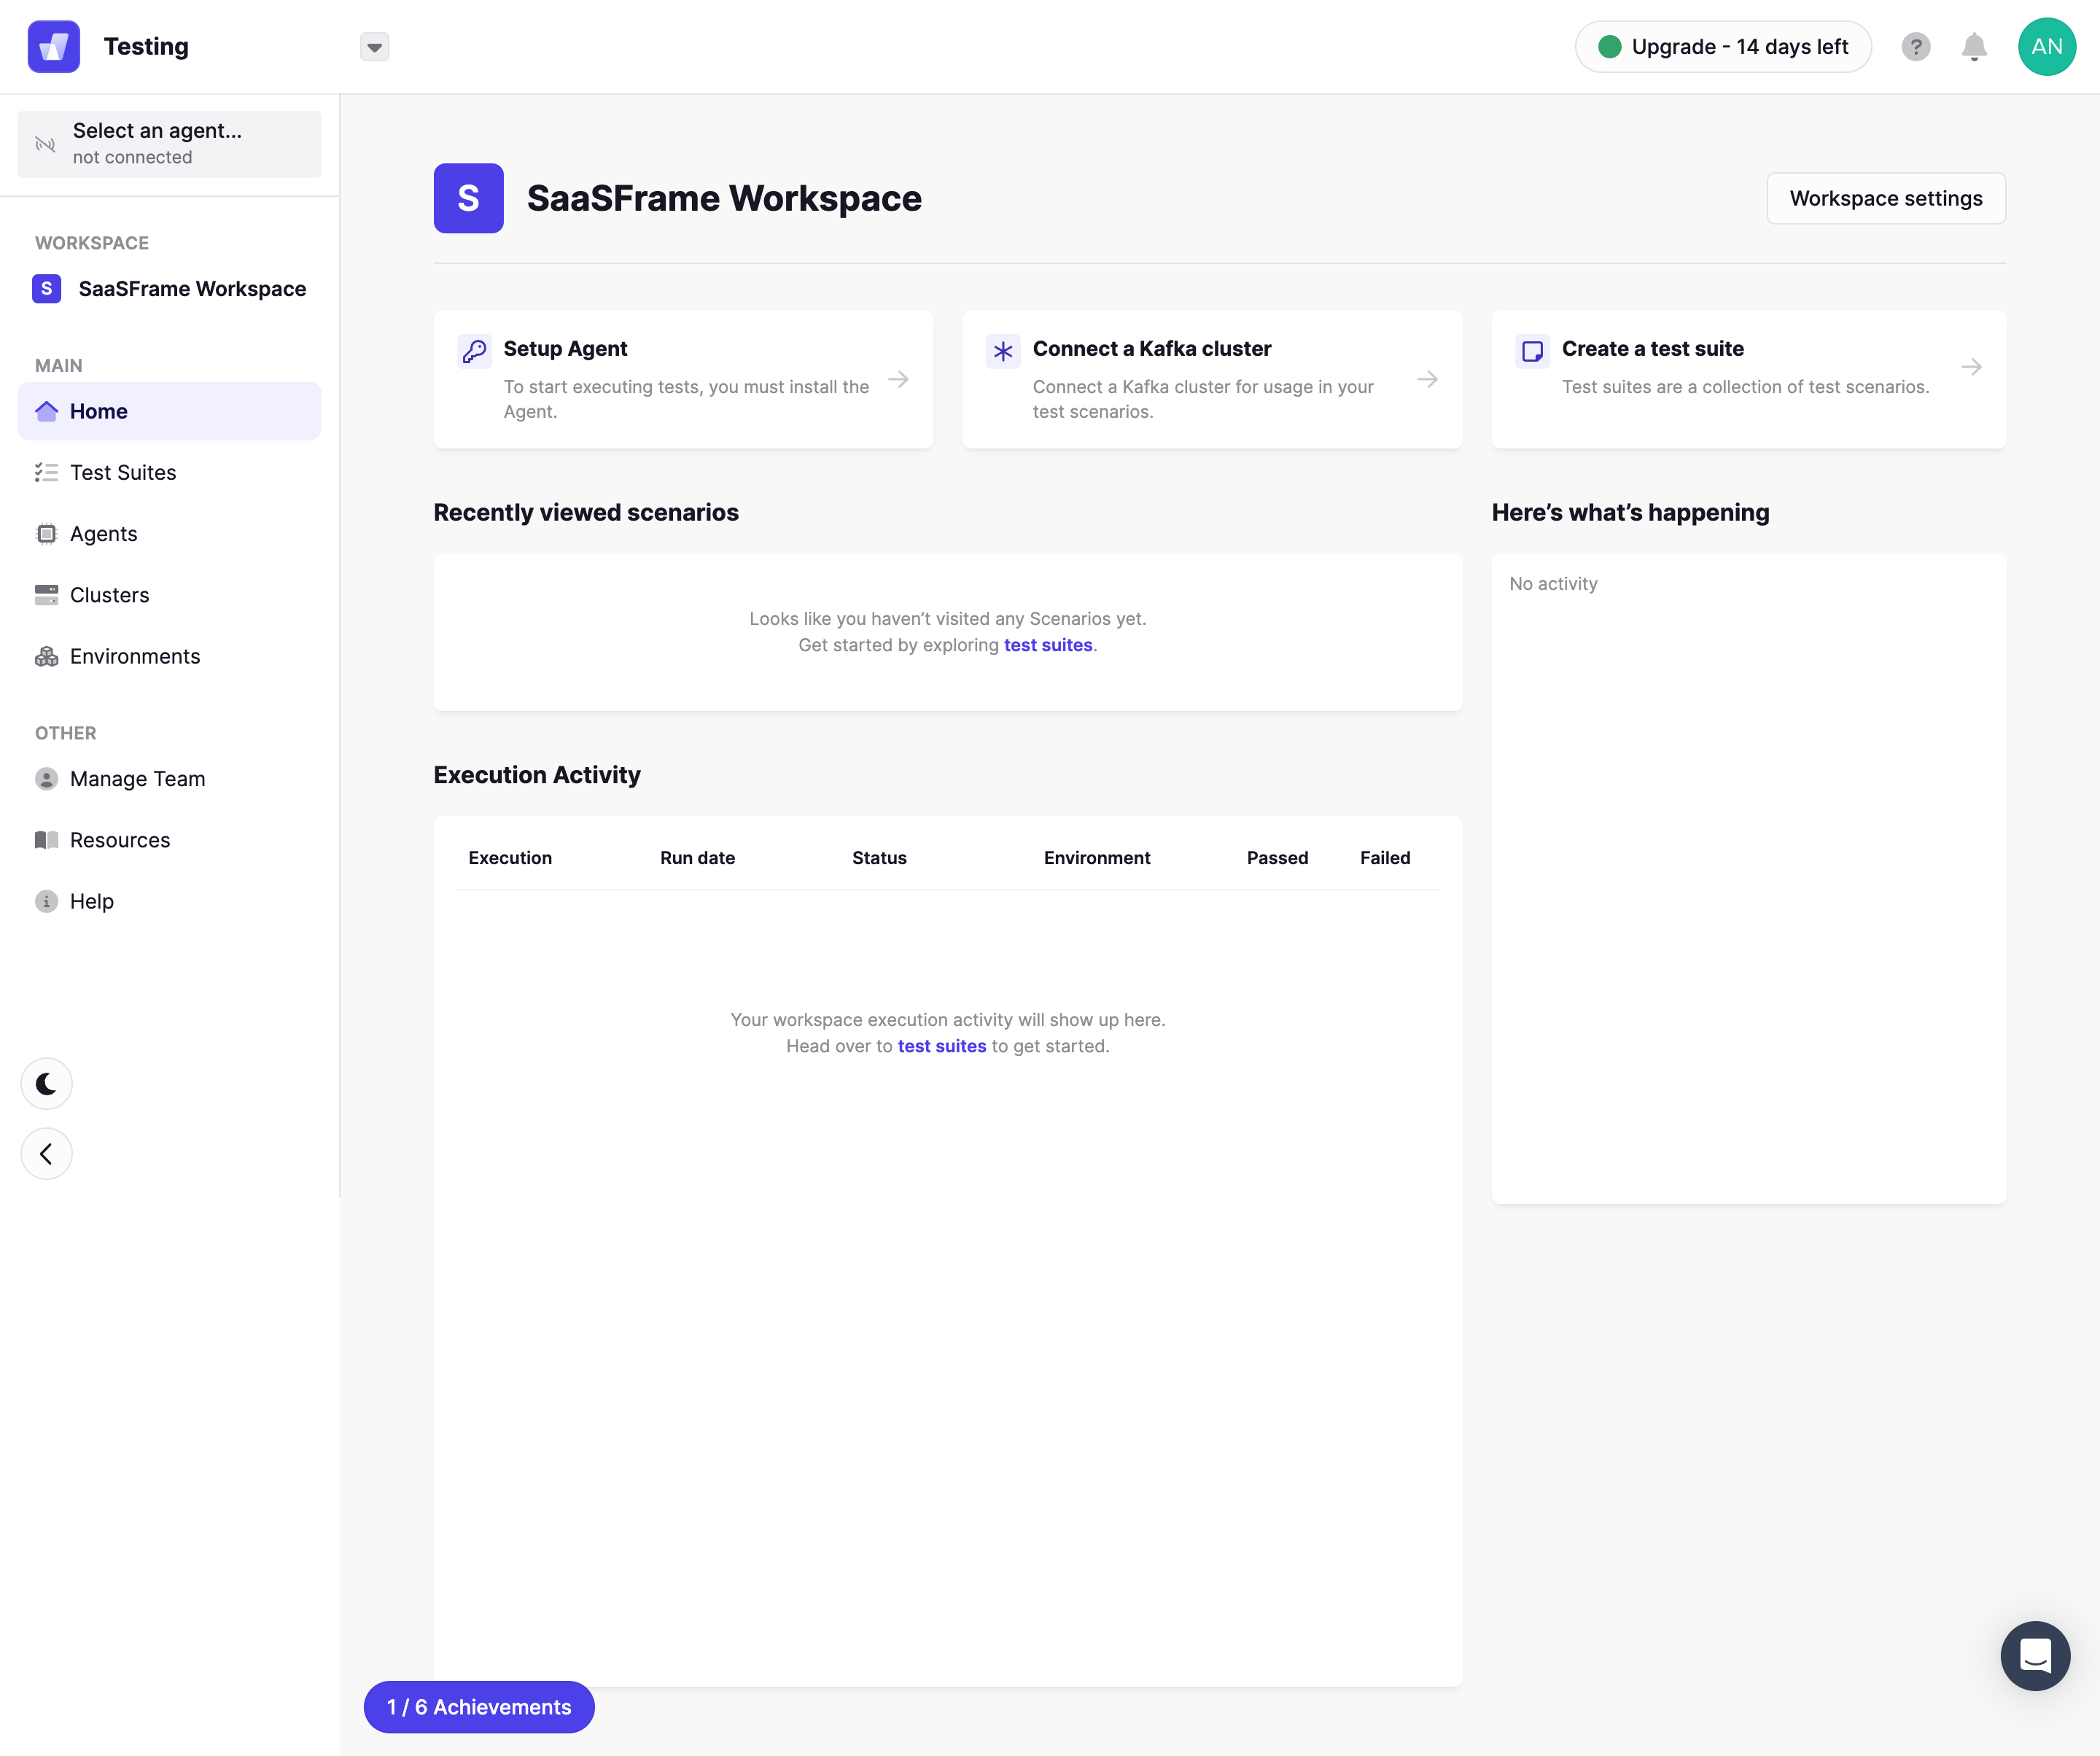
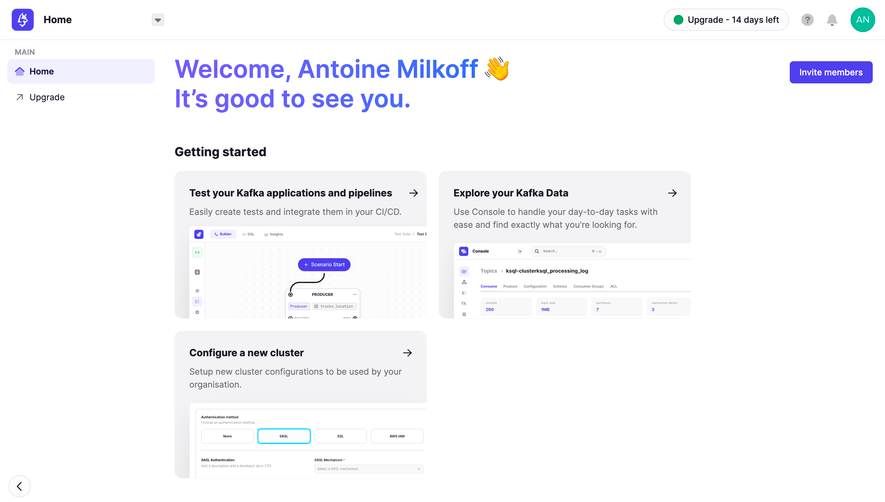
Testing Agent 1 not connected WORKSPACE SaaSFrame Workspace MAIN Home Test Suites o Agents Clusters Environments OTHER Manage Team r Resources Help Upgrade - 14 days left AN Agents Latest: 0.38.0 Personal Agent 1 Created a few seconds ago 1 / 6 Achievements Setup agent + Create an agent 0 NOT CONNECTED
API Management
Observability & Monitoring

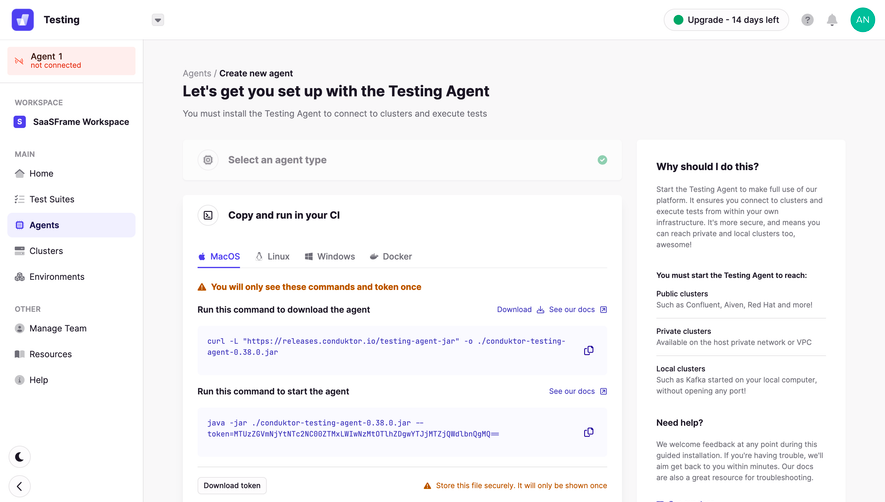
Create Element
Conduktor
Add & Edit
Product
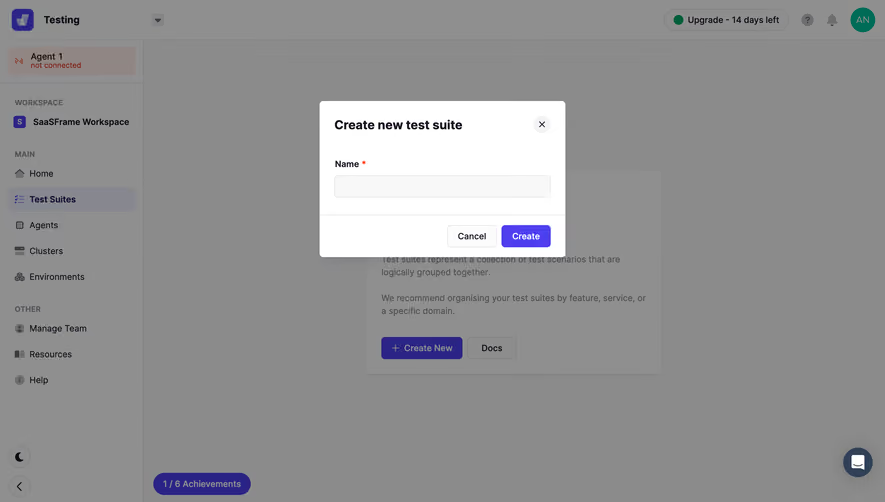
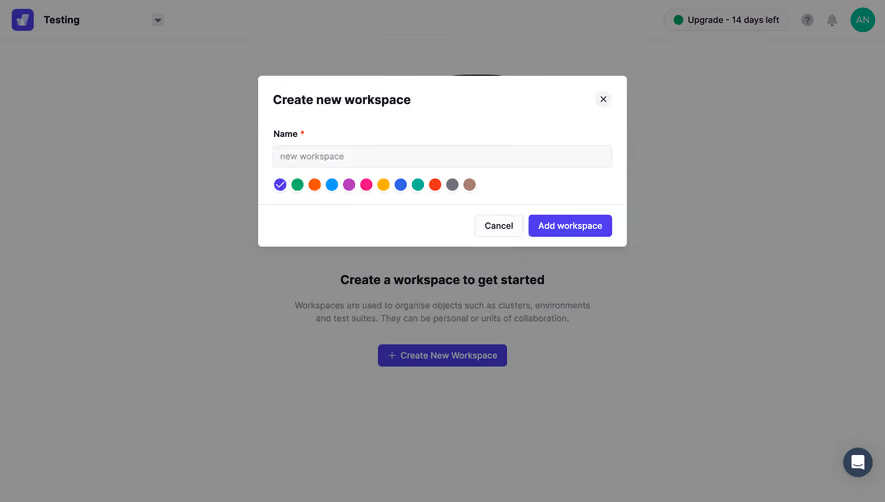
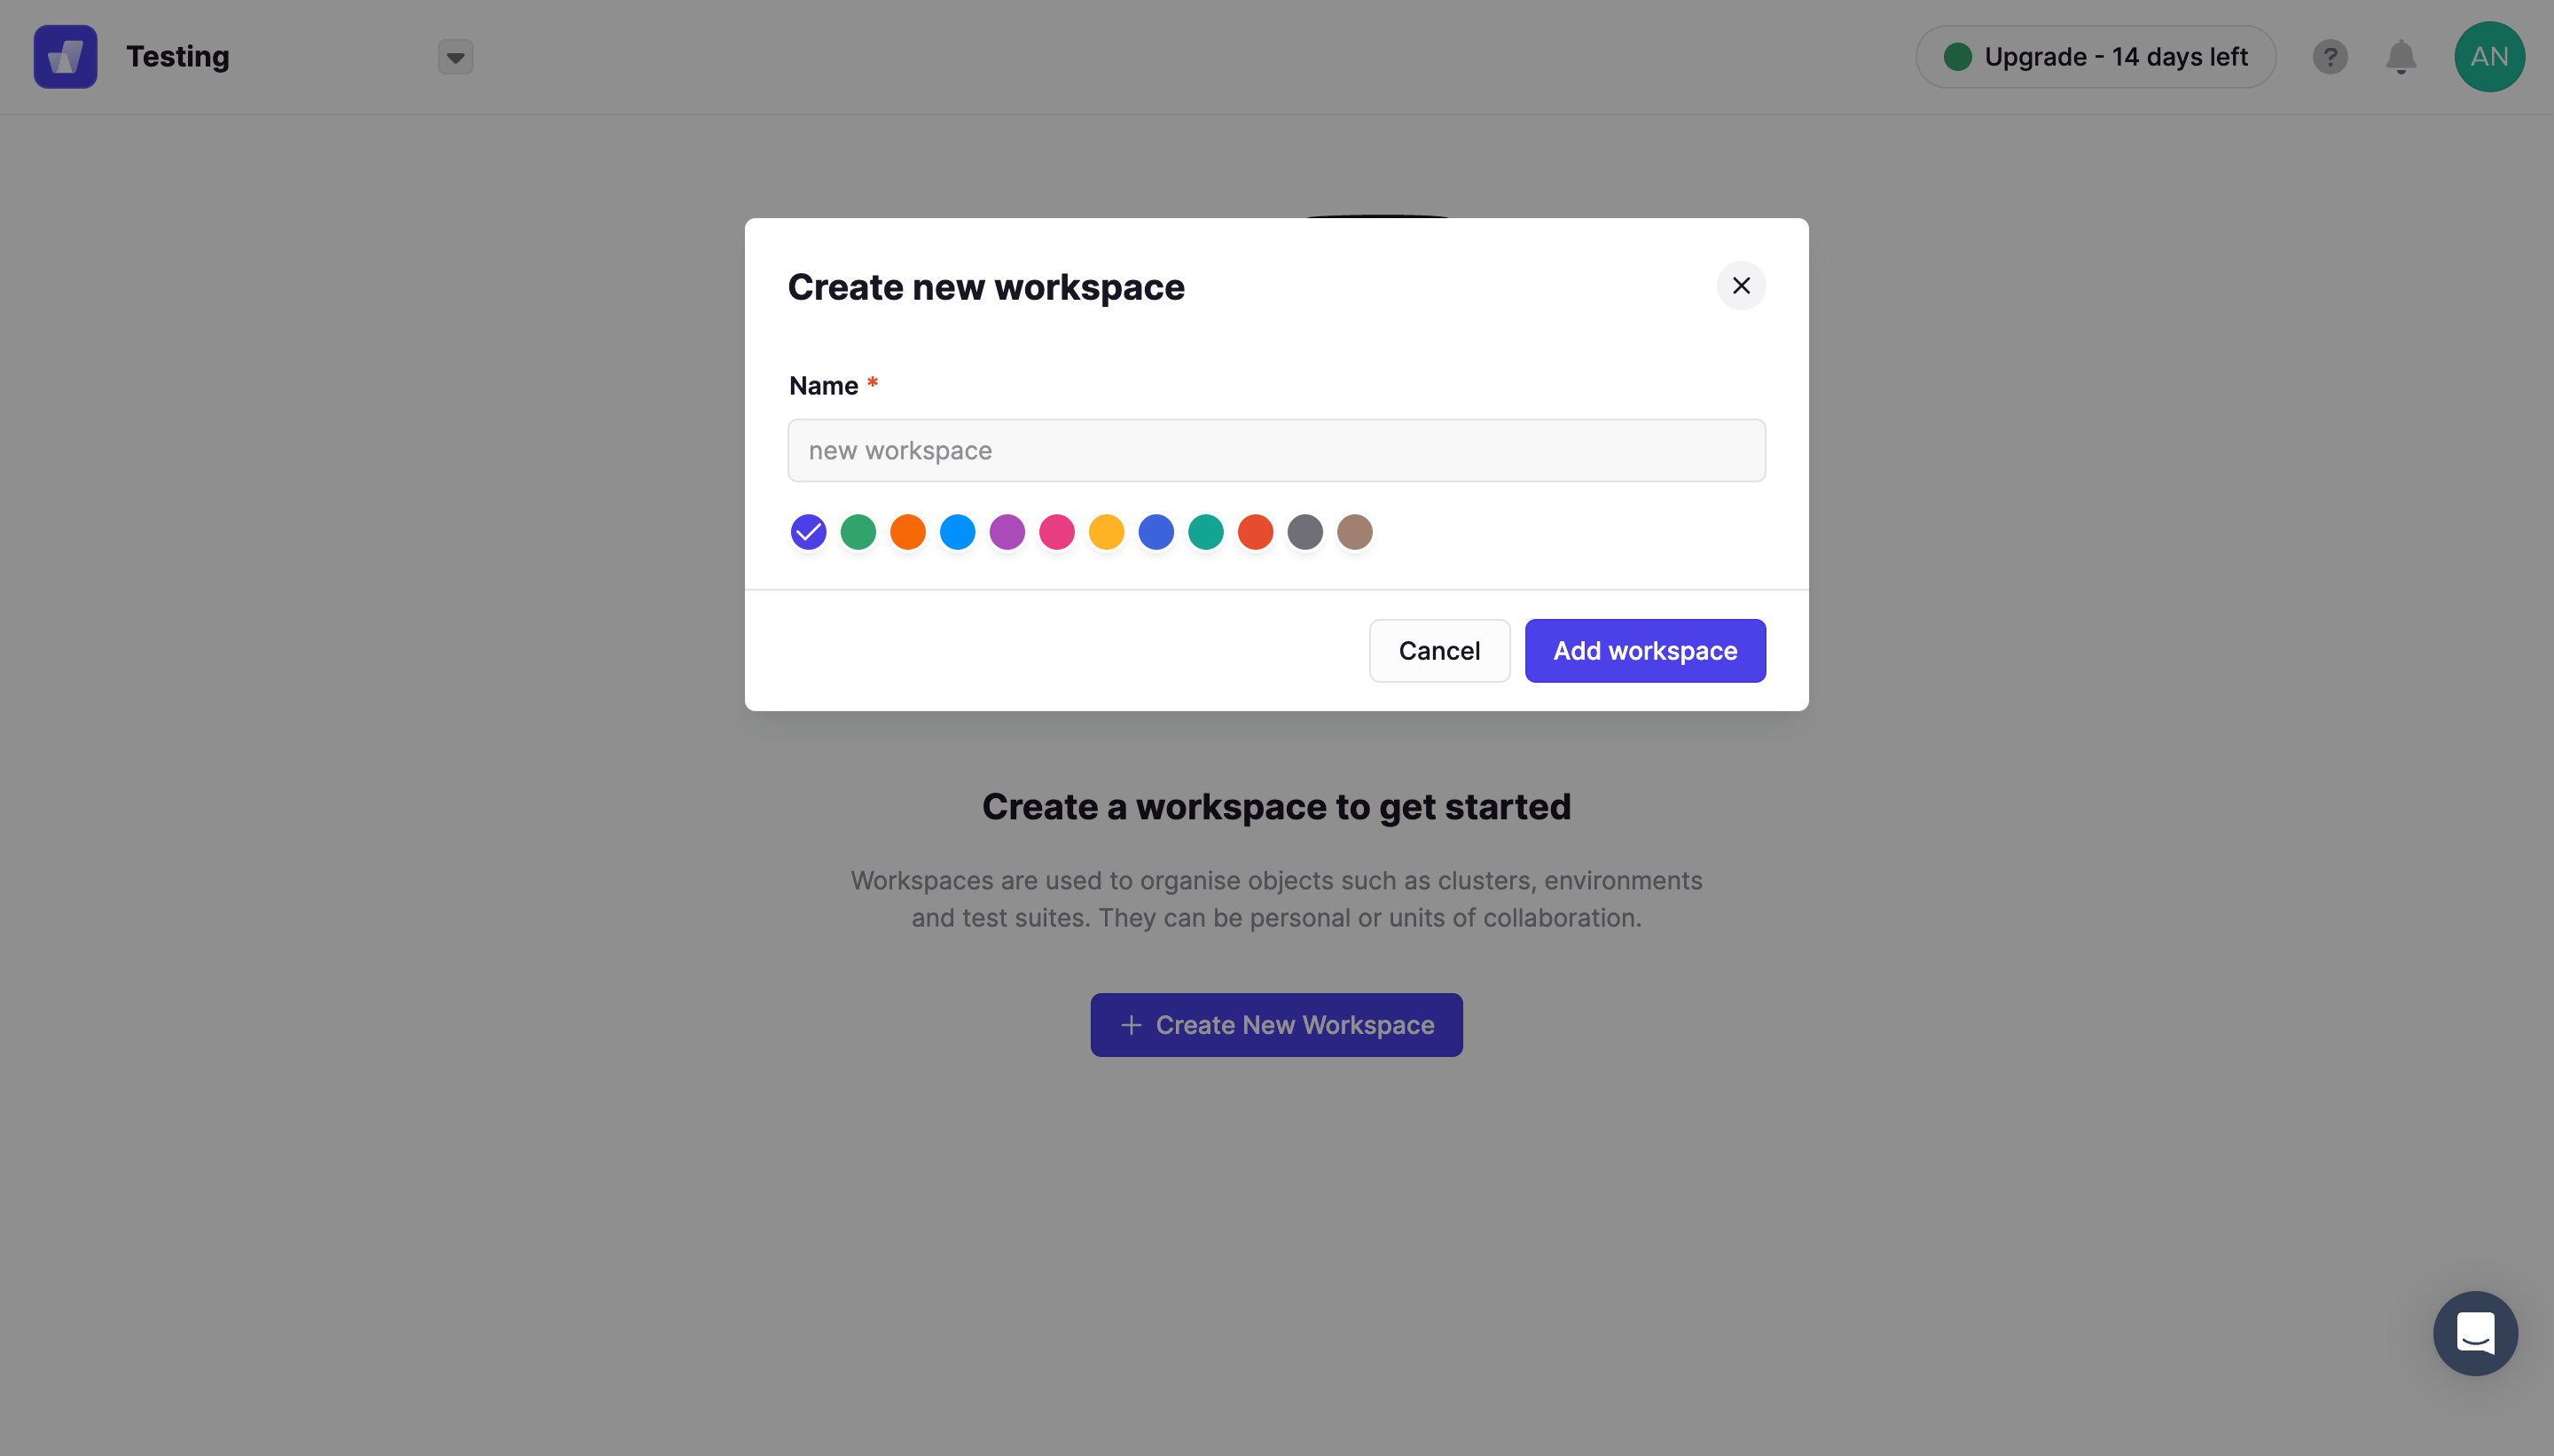
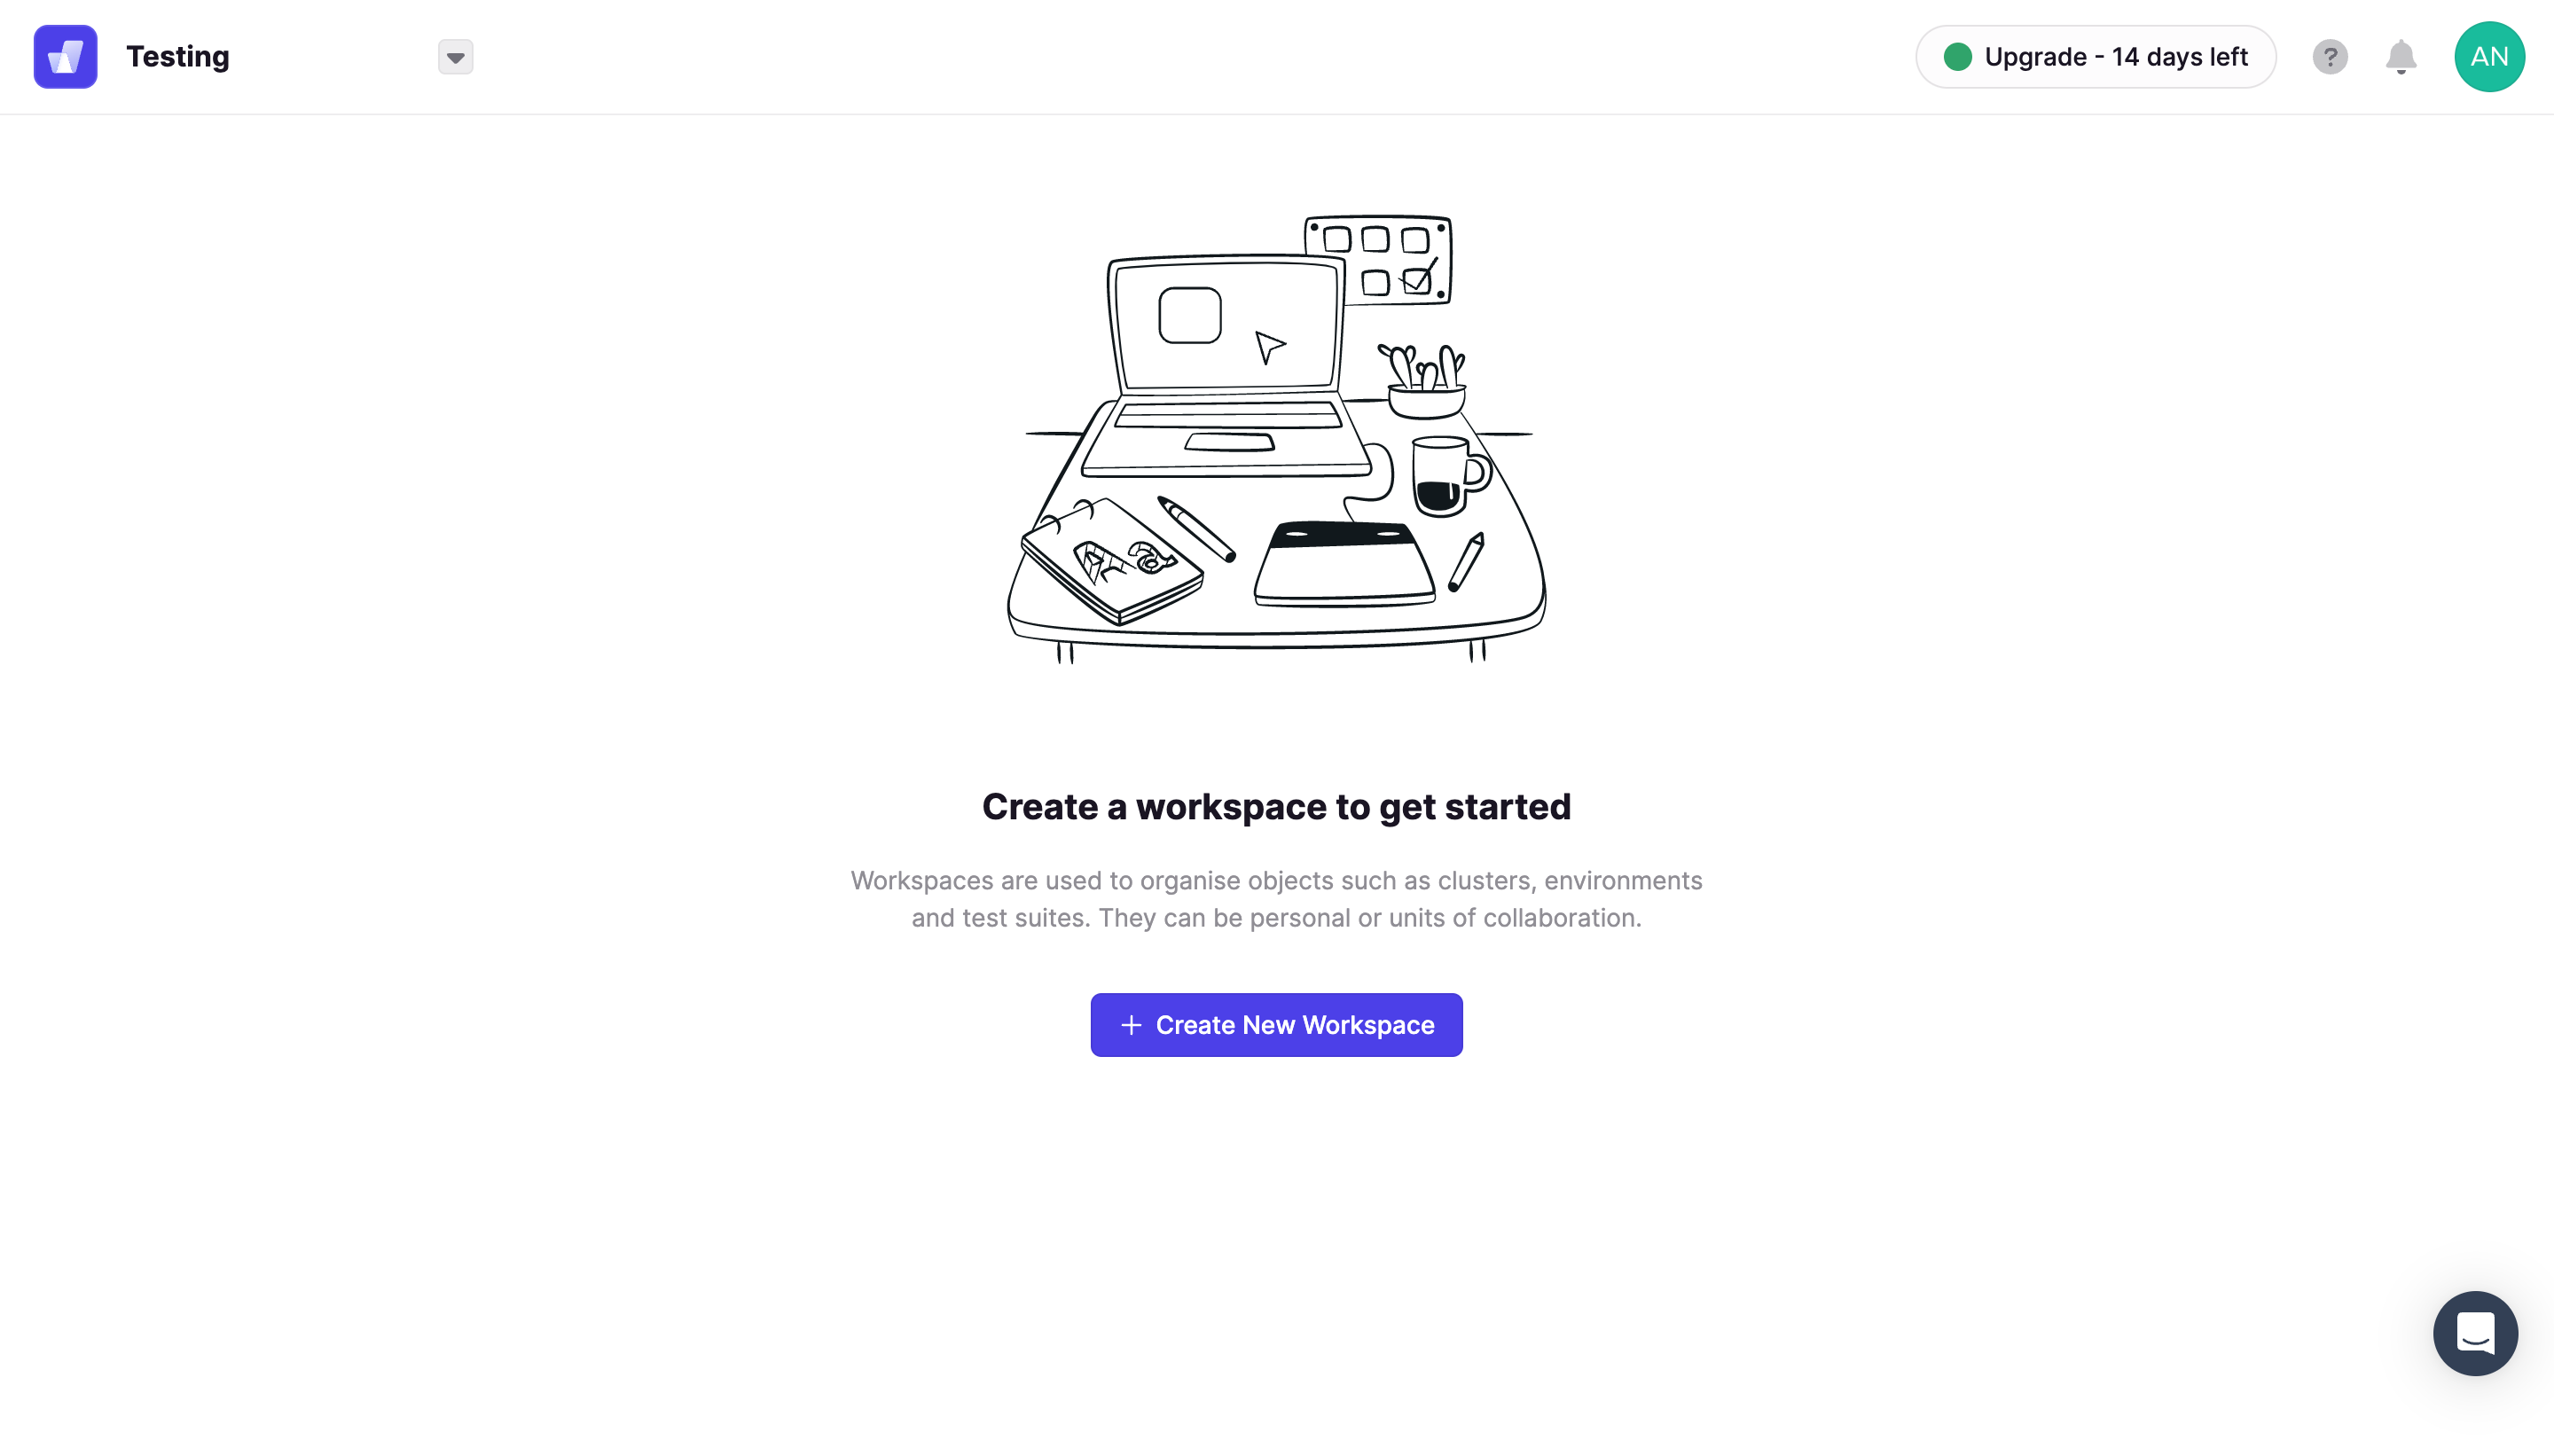
Upgrade - 14 days left Testing Create new workspace x Name * new workspace eooooooooooo Cancel Add workspace Create a workspace to get started Workspaces are used to organise objects such as clusters, environments and test suites. They can be personal or units of collaboration. + Create New Workspace
API Management
Observability & Monitoring
Create Element
Conduktor
Add & Edit
Product
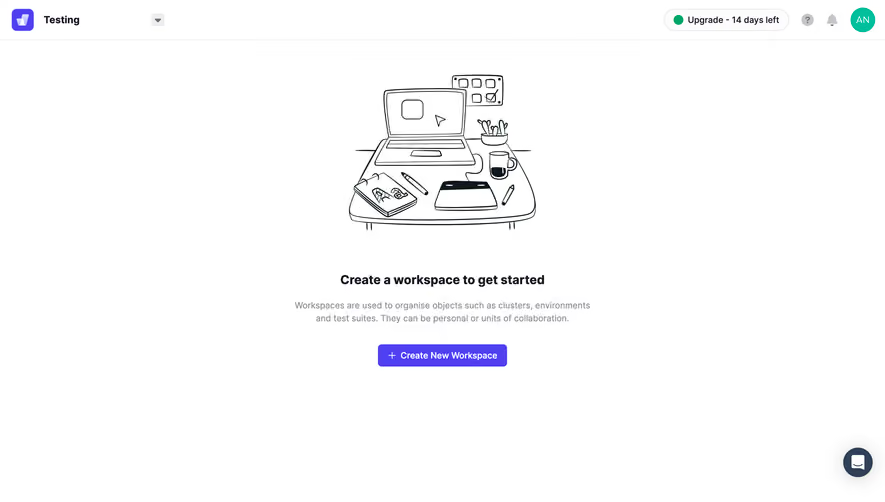
Testing Upgrade - 14 days left AN •ooo• Create a workspace to get started Workspaces are used to organise objects such as clusters, environments and test suites. They can be personal or units of collaboration. + Create New Workspace
API Management
Observability & Monitoring


Invite Team Members
Conduktor
Invite Team Members
Product
conduktor Welcome aboard Organisation setup Team invitation -5 Invite your team Who do you want to collaborate with? Invite via email * [email protected] Invite link Share this link to invite anyone to your Copy link organisation. Send invite Skip for now
API Management
Observability & Monitoring


Account Setup
Conduktor
Discovery Questions
Product
conduktor Welcome aboard Organisation setup Team invitation -5 Create an organisation Collaborate with your team by creating an organisation. Your company name * EB e.g. Conduktor How many people work with Kafka in your organisation? Less than 10 Organisation URL Continue conduktor.app
API Management
Observability & Monitoring

Account Setup
Conduktor
Account Setup
Product
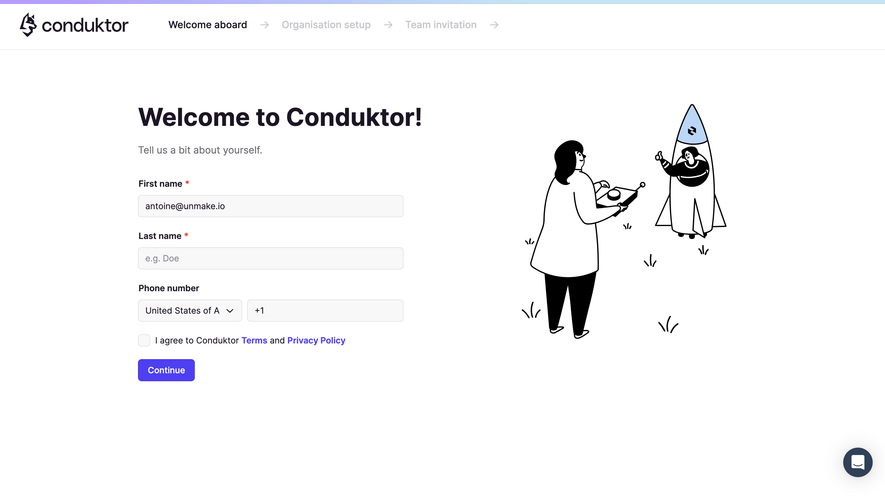
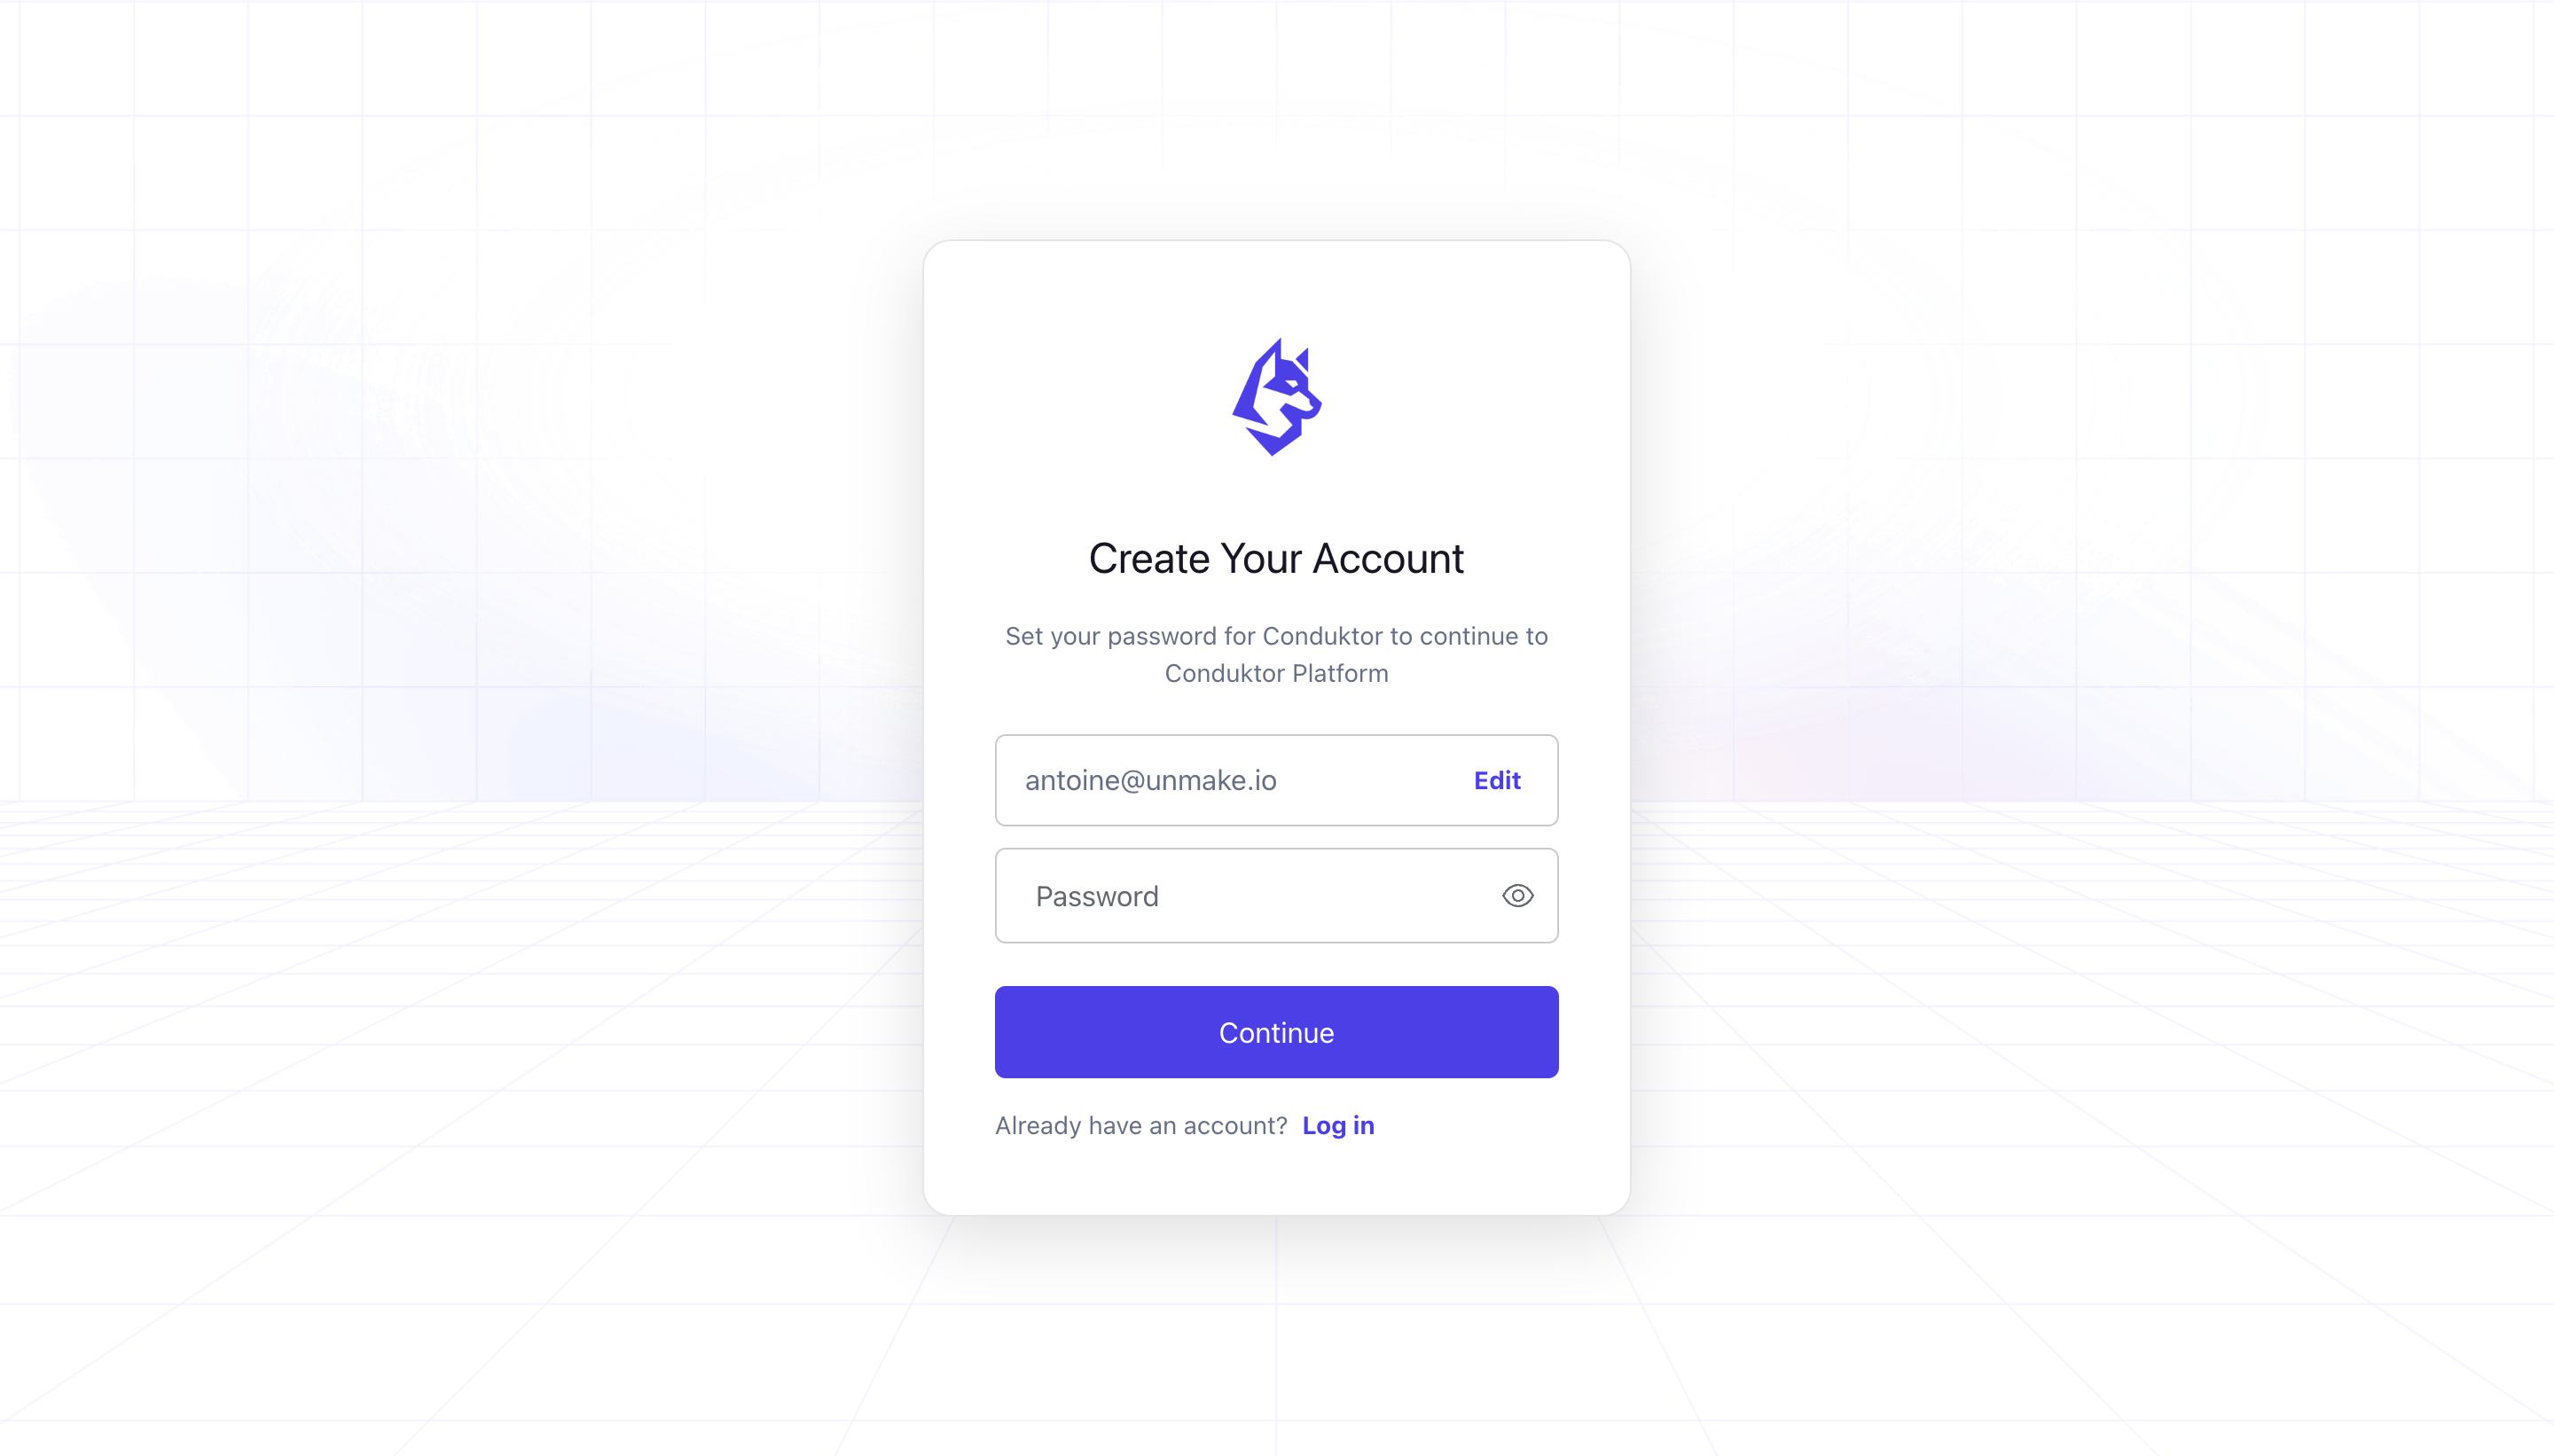
conduktor Welcome aboard Organisation setup Team invitation -5 Welcome to Conduktor! Tell us a bit about yourself. First name * [email protected] Last name * e.g. Doe Phone number United States of A v I agree to Conduktor Terms and Privacy Policy Continue
API Management
Observability & Monitoring









Upgrade to SaaSFrame Pro to browse all screens
Monthly
$18 /month
Billed $18 monthly
Browse all screens & flows
Filter and search screens & flows
Search text in screenshots
Access Figma files
Access mobile versions
Join now
Quarterly
$16 /month
Billed $48 quarterly
Browse all screens & flows
Filter and search screens & flows
Search text in screenshots
Access Figma files
Access mobile versions
Join now
Yearly
$15 /month
Billed $180 yearly
Browse all screens & flows
Filter and search screens & flows
Search text in screenshots
Access Figma files
Access mobile versions
Join now