 SaaSFrame
⚙️ Settings
Organize complex preferences with intuitive SaaS Settings and Configuration UI layouts. From categorized sidebar navigation to toggle-heavy preference panels, discover how to make deep software settings easy to browse.

Index of all 238 Settings examples
- Caveman Account Settings
- Latent Escalation Policy
- Latent Project Settings
- Composal Project Settings
- Composal Environments
- AskAiRank LLM Providers Settings
- AskAiRank Brand Settings
- Rox Notification Settings
- Rox Integrations Settings
- Rox General Settings
- Rox Account Menu
- Rox Automation Editor
- Rox Sequence Settings
- Rox Sequence AI Tuning
- Privacyboard Settings
- Privacyboard Company Profile
- Privy Funding Methods
- Privy Authentication Login Methods
- Privy UI Components Branding
- Datashake API Keys
- Respan Billing
- Voiceflow Agent Global Prompt Editor
- Unabyss Security Settings
- Unabyss Profile Settings
- Moss Workspace general settings
- Moss Index access and deletion settings
- Dub Configure conversion tracking
- Dub API keys overview
- Dub Workspace general settings
- Dub Default domains
- Pangram Account settings
- Tines Audit Log
- Tines AI Model & Spend Settings
- Tines Personal Preferences
- Tines Member Access Permissions
- Tines Member Profile & Roles
- Lightspark Enforce SSO Domain
- Lightspark Account & Security Settings
- Context.dev Billing Settings
- EigenPal Data retention settings
- Hugging Face Storage bucket settings
- Hugging Face Preferred hardware settings
- Hugging Face Notification settings
- Hugging Face Organization settings
- Hugging Face Authentication settings
- Hugging Face Account settings
- Hugging Face Profile settings
- Hugging Face Repository advanced settings
- Hugging Face Repository settings
- GraphCMS File field editor with success notification
- GraphCMS Content model fields list
- GraphCMS File field configuration form
- GraphCMS Content model field configuration
- NewsCatcher Settings
- Cloudflare Speed Settings
- Cloudflare Security Settings
- Claude Privacy Controls
- Claude Connector Details
- Claude Capabilities Settings
- Claude Privacy Settings
- Claude Account Settings
- Claude General Settings
- Dust Workspace Settings
- Dust Connections Admin
- Dust Settings
- Prelude Messages Configuration
- Unkey API Settings
- Visitors Security Settings
- Visitors Project Settings
- Visitors Manage Account
- Hume AI Account Settings
- Hume AI API Keys
- Wise Settings
- Checkout.com Team Permissions
- Superlist Subscriptions Settings
- Superlist Features Settings
- Superlist Profile Settings
- GoFundMe Account Settings
- Steep Workspace Settings
- Steep Targets
- Wiza Account Settings
- Wiza Profile Settings
- Mintlify Add Custom Domain
- Mintlify Settings
- Intercom Install Messenger
- Intercom Article Settings
- Oku Settings
- Uvodo Brand Settings
- Uvodo Brand Settings
- Uvodo General Settings
- Uvodo Product Settings
- Remote Company Settings
- Remote Time Tracking
- FlowMapp General Settings
- Hyperline Payment Settings
- Hyperline Payment Settings
- Hyperline General Settings
- Hyperline General Settings
- Copperx Business Settings
- Copperx Settings
- Copperx Add Payment Method
- Cal.com API Keys Settings
- Cal.com API Keys Settings
- Cal.com Webhooks Settings
- Cal.com Password Settings
- Cal.com Conferencing Settings
- Cal.com Calendars Settings
- Cal.com General Settings
- Cal.com Profile Settings
- Cal.com Availabilities Settings
- Vidzflow Profile Settings
- Frame Notifications Settings
- Frame Profile Settings
- Frame Company Settings
- Frame Company Settings
- Rise Working Hours Settings
- Rise General Settings
- Expertpage Domain Settings
- Plausible Analytics Visibility Settings
- Plausible Analytics General Settings
- Meiro Account Settings
- Loops Email Campaign Recap
- Loops Email Campaign Scheduling Settings
- Loops Email Campaign Scheduling Settings
- Loops Email Campaign Contact Settings
- Routine Advanced Settings
- Supabase Auth Settings
- Supabase API Settings
- Supabase Database Settings
- Supabase General Settings
- Livestorm Event Recording Settings
- Livestorm Event Emails Settings
- Livestorm Event Room Settings
- Livestorm Event Registration Settings
- Livestorm Event General Settings
- Linktree Settings
- Popwork Users & Roles
- Assembly Notification Settings
- Current Weekly Drop Settings
- Current Rituals Settings
- Current Streams Settings
- Current Members Settings
- Current Workspace Settings
- Folio Integration Settings
- Folio Members Settings
- Clay Organizations Settings
- Clay Social Settings
- Clay Profile Settings
- Clay Settings
- WorkOS Admin Portal Configuration
- WorkOS Empty Audit Log
- WorkOS Directory Sync Configuration
- WorkOS Configuration Settings
- Dokably Settings
- Mercury Security Settings
- Mercury Notifications Settings
- Mercury Company Settings
- Phantombuster Workspace Settings
- Phantombuster User Settings
- Formcarry Account Settings
- Formcarry Form Settings
- Luma Notifications Settings
- Luma Security Settings
- Luma Preferences Settings
- Luma Account Settings
- Cohere API Settings
- Threads Settings
- SavvyCal Links Settings
- SavvyCal Profile Settings
- Pirsch Analytics Account Settings
- Pirsch Analytics Danger Zone Settings
- Pirsch Analytics Import/Export Settings
- Pirsch Analytics Integration Settings
- Pirsch Analytics Access Settings
- Pirsch Analytics General Settings
- Zencal Profile Settings
- Better Stack etter Uptime Account Settings
- Better Stack etter Uptime API Settings
- Nord VPN Notification Preferences
- Nord VPN Multi-factor authentication Settings
- Nord VPN Account Details
- Hotjar Referral Settings
- Hotjar Account & Security Settings
- Lemon Squeezy Account Settings
- Lemon Squeezy Affiliates Settings
- Lemon Squeezy Email Settings
- Lemon Squeezy Webhook Settings
- Lemon Squeezy General Settings
- Logbook Project Settings
- Logbook Team Settings
- Logbook Security Settings
- Logbook Notifications Settings
- Logbook Location Settings
- Logbook Profile Settings
- Café Settings
- Coherence Settings
- Folk Google Account Connected
And 38 more in the library.
⚙️ Settings: design guide
Short answer
SaaS settings turn preferences and admin controls into understandable decisions. Organise them by responsibility (personal, workspace, billing), say who a change affects, make save behaviour predictable, explain requirements next to advanced controls and show permission-limited options with the reason.
In the libraryas of November 2026
- Screens
- 238
- SaaS products
- 92
- Last added
- Nov 2026
Common patternsSettings & Preferences 180Text Input 109Toggle 72Sidebar Navigation 51Dropdown Menu 48
SaaS settings turn a collection of preferences and administrative controls into decisions people can understand. A useful settings interface makes the affected scope, permission requirements, and save behavior clear before users change anything.
The SaaSFrame captures below show team privacy, personal preferences, and organizational authentication. Their differences explain why a settings page needs more than a tidy list of toggles.
How should settings be organised?
Personal, workspace, and organization settings may look similar but affect different people. Establish the scope through navigation, headings, and contextual explanation.
Group controls around tasks users recognize: profile, notifications, billing, team access, or security. Avoid grouping only by the internal service that stores a value.
Provide stable routes to common tasks. A user changing a notification preference should not need to inspect several broadly labeled administration tabs first.
Explain who a change affects
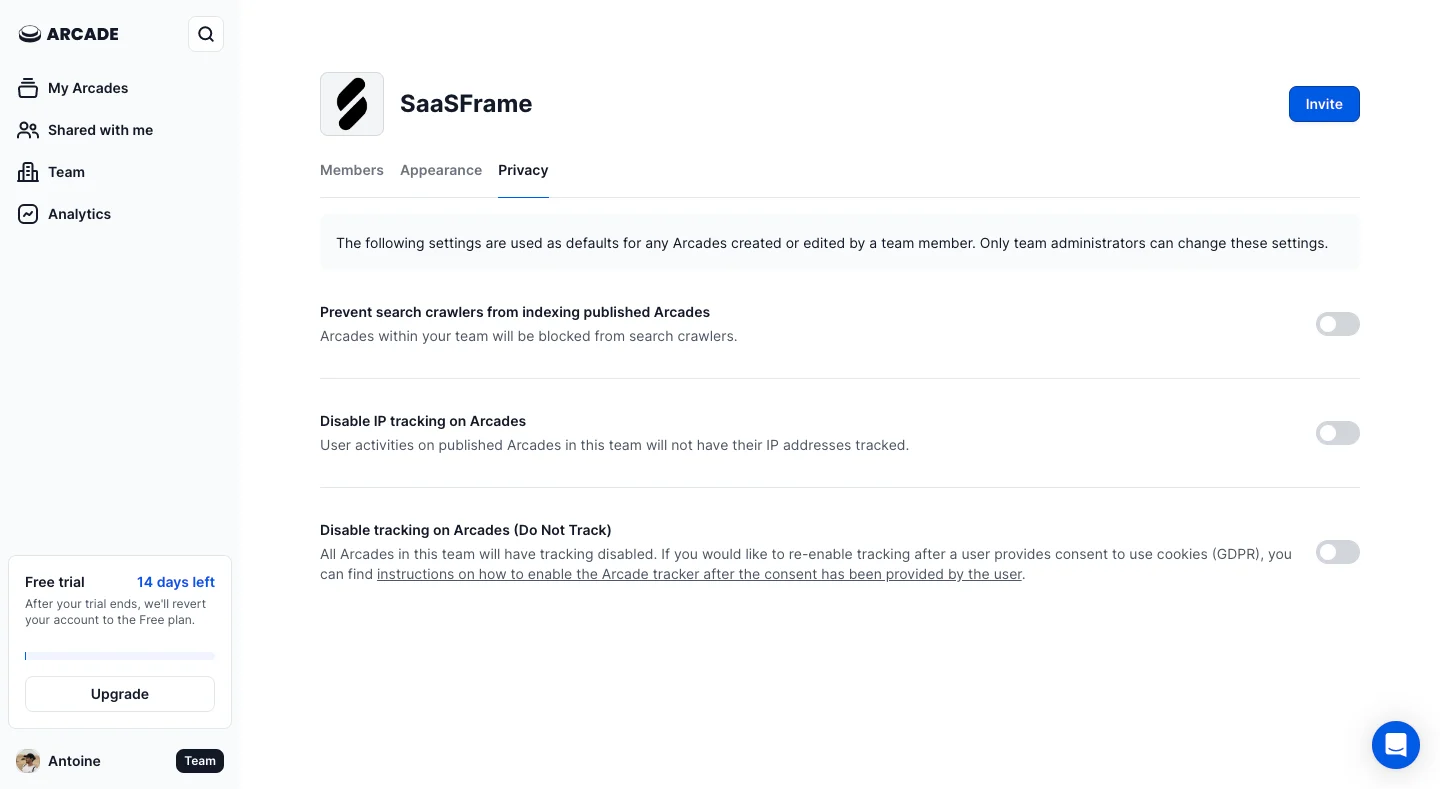
The Arcade team-privacy capture presents toggles for search indexing and tracking with supporting explanation. The page indicates team-level settings and includes role-related context.
A switch looks simple, but its scope can be substantial. Text beside the control should explain whether the value affects the current person, future content, all existing content, or a team default.
Where administrators control a shared policy, distinguish the policy from a personal preference. Users should understand whether they can change a setting themselves or need a team administrator.
Separate unrelated actions within a profile
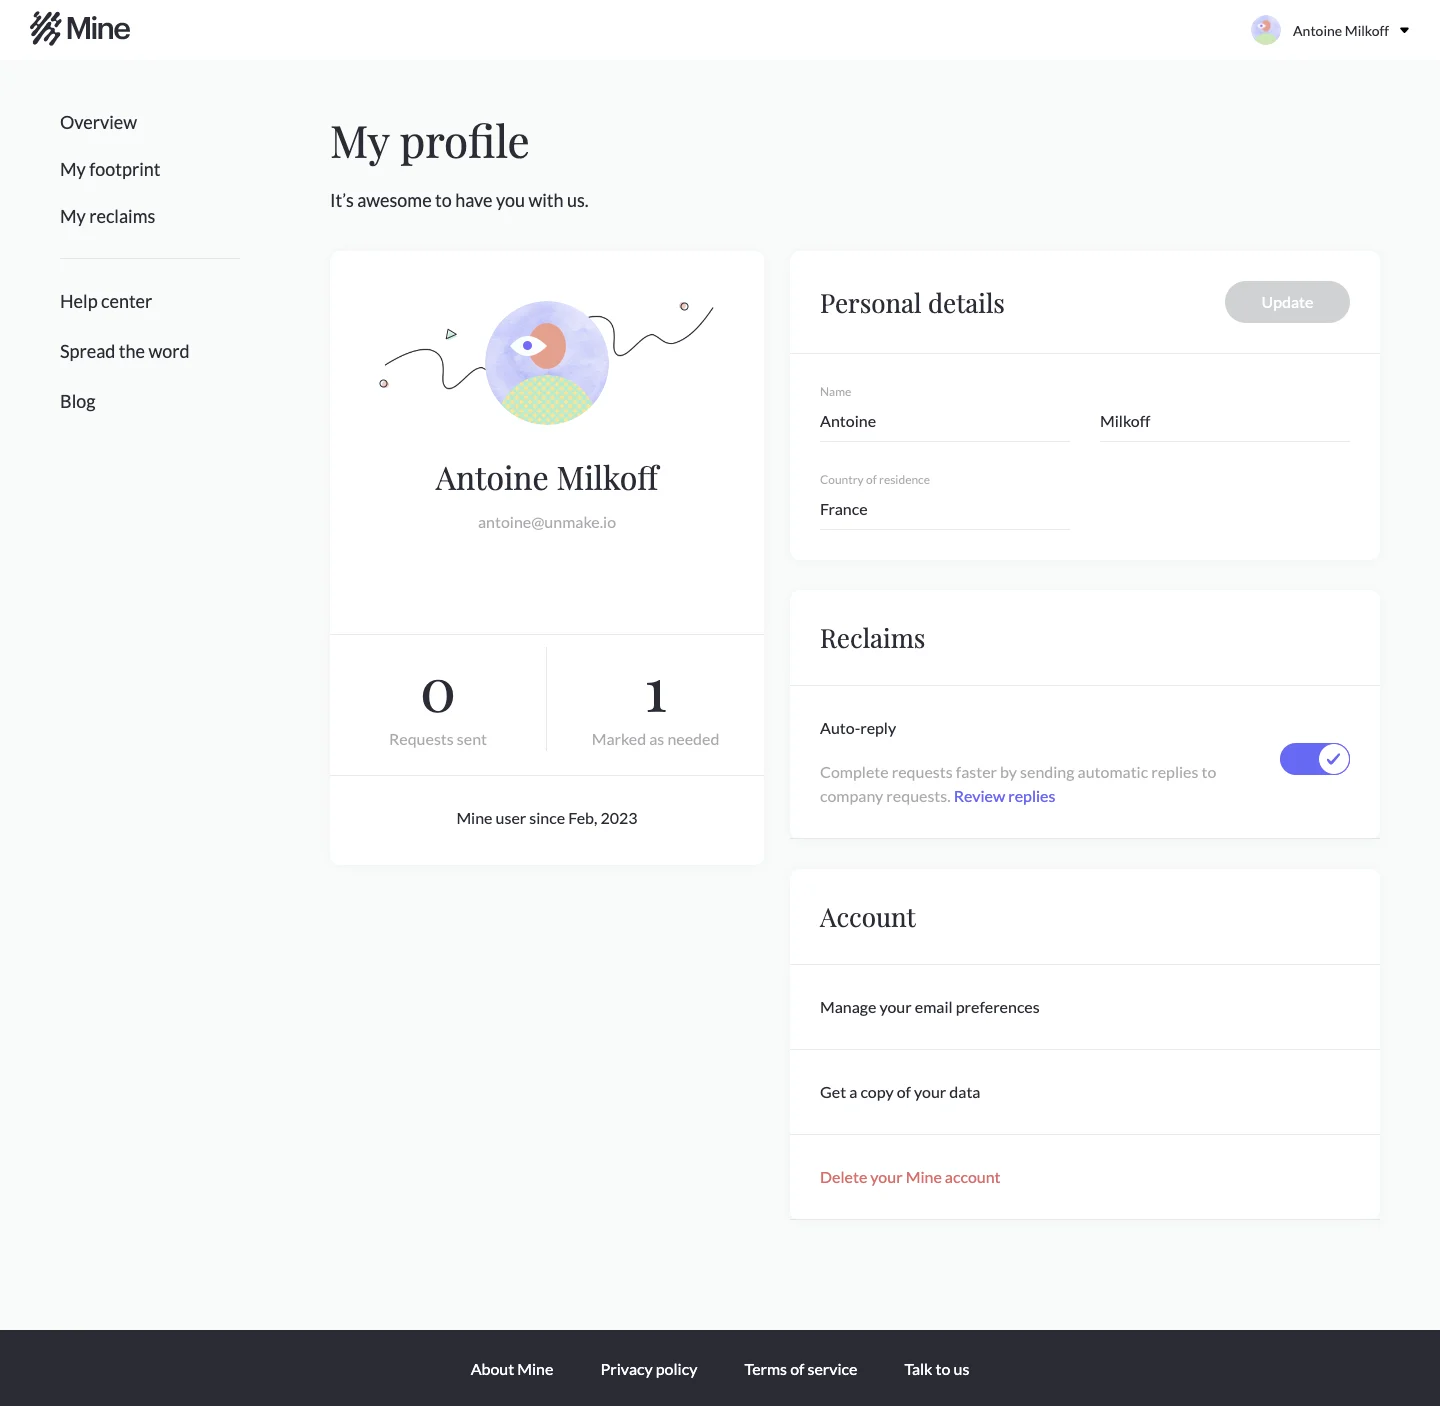
The Mine profile reference combines personal details with separate controls for automation, email preferences, data export, and account deletion. These tasks have different consequences even though they share the settings area.
Use sections and explicit actions to keep that distinction readable. Updating a name should not appear to submit an unrelated automation preference or request account deletion.
When several sections save independently, show the relevant save control and feedback within each section. If a page saves everything together, make that page-wide scope equally clear.
Make save behavior predictable
A toggle can save immediately, while a form may require submission. Mixed models can work when the interface communicates them consistently.
Provide visible feedback for pending changes, successful persistence, and failure. Do not leave users guessing whether a switch updated a stored preference or only changed the local screen.
Handle navigation away from unsaved changes according to the actual model. If the change is already saved, an unsaved-warning dialog is misleading; if it is pending, silent loss is equally confusing.
Explain requirements beside advanced controls
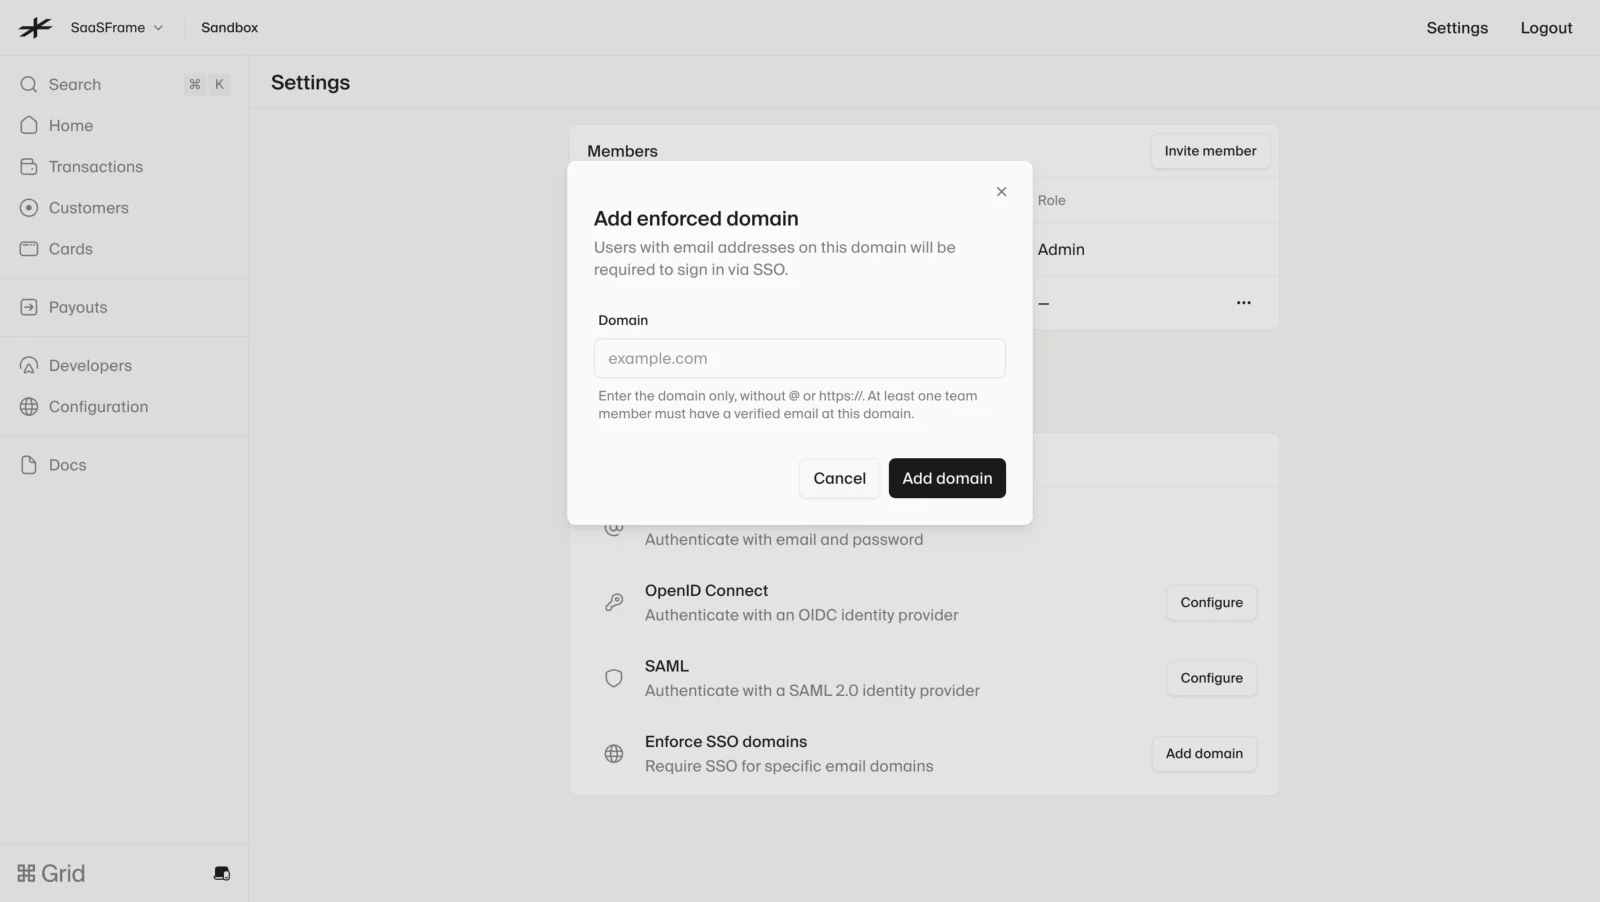
The Lightspark domain-enforcement dialog explains the domain format and a prerequisite involving a verified member. It appears over authentication settings and provides distinct cancel and add-domain actions.
This places preparation and input guidance at the decision point. An advanced control should explain the specific requirement users can resolve rather than sending them to a general documentation page with no direction.
Organization authentication also needs scope clarity. Explain whose access changes and when the policy takes effect using the product's real behavior. The capture demonstrates the dialog structure, not a guarantee about its implementation.
Keep permission-dependent controls understandable
A settings page may be visible to people who cannot edit every value. Make read-only states explain the required role or responsible administrator where appropriate.
Avoid showing an active-looking action that fails only after submission when the missing permission is already known. Conversely, hiding all evidence of a policy can make its effects impossible to understand.
Review role changes while a page is open. A user may begin editing with one permission state and submit after it changes. The result needs a clear explanation.
Use defaults as explicit decisions
Defaults should be understandable and appropriate to the scope. A team-wide default may influence new objects without overriding existing ones; a personal preference may apply immediately.
Explain inheritance where it matters. Users should be able to identify whether they are editing their own value, inheriting a workspace setting, or overriding an organization policy.
Reset actions need similarly precise language. Restoring a default is not always the same as clearing a field or removing an override.
Help users find consequential controls
Search can support a large settings area, but good grouping and direct labels remain necessary. Search results should identify the section and scope rather than displaying detached control names.
Keep high-impact operations visually distinct from ordinary preferences. Profile editing, access-policy changes, billing actions, and deletion should not share an indistinguishable generic save button.
If an action requires a separate confirmation, explain why through its consequences. Additional steps should support a decision rather than merely create friction.
Validate the settings lifecycle
Review initial values, edits, submission, failure, refreshed state, and permission changes. A locally successful interaction is incomplete if the value does not persist after reload.
Check labels, keyboard navigation, focus, and assistive-technology feedback. Toggle state and explanatory text must be available without relying on color or pointer interaction.
Explore SaaSFrame's settings references to compare scope and grouping. Use the examples to shape clear decisions around your own product's responsibilities.
Settings design questions
Should settings save automatically?
Either automatic or explicit saving can work. Make the chosen model visible and consistent, especially when several independent sections share a page.
How should personal and team settings differ?
Name the affected scope and organize controls around the responsible user or role. Explain inheritance when a personal value depends on shared policy.
What makes an advanced setting understandable?
Give the consequence, requirements, input guidance, and recovery route at the point of use. The control label alone is rarely enough.